How to renew SSL certificate coverage in 2026 comes down to automation: let your host, your CDN or Certbot renew it for you. A paid certificate is the one case where you still order and install the renewal by hand.
We checked every date in this guide against the CA/Browser Forum, Let’s Encrypt, Certbot, cPanel, Cloudflare and WordPress documentation in October 2026. We also read the live certificates of 13 large sites and our own, and we tested the WordPress steps on a WordPress 7.1 test site.
You will see how long certificates last now and how to check your expiry date. Then come three renewal methods, the WordPress checks to run after renewing, and fixes for a failed or expired certificate.
How Long Does an SSL Certificate Last in 2026?
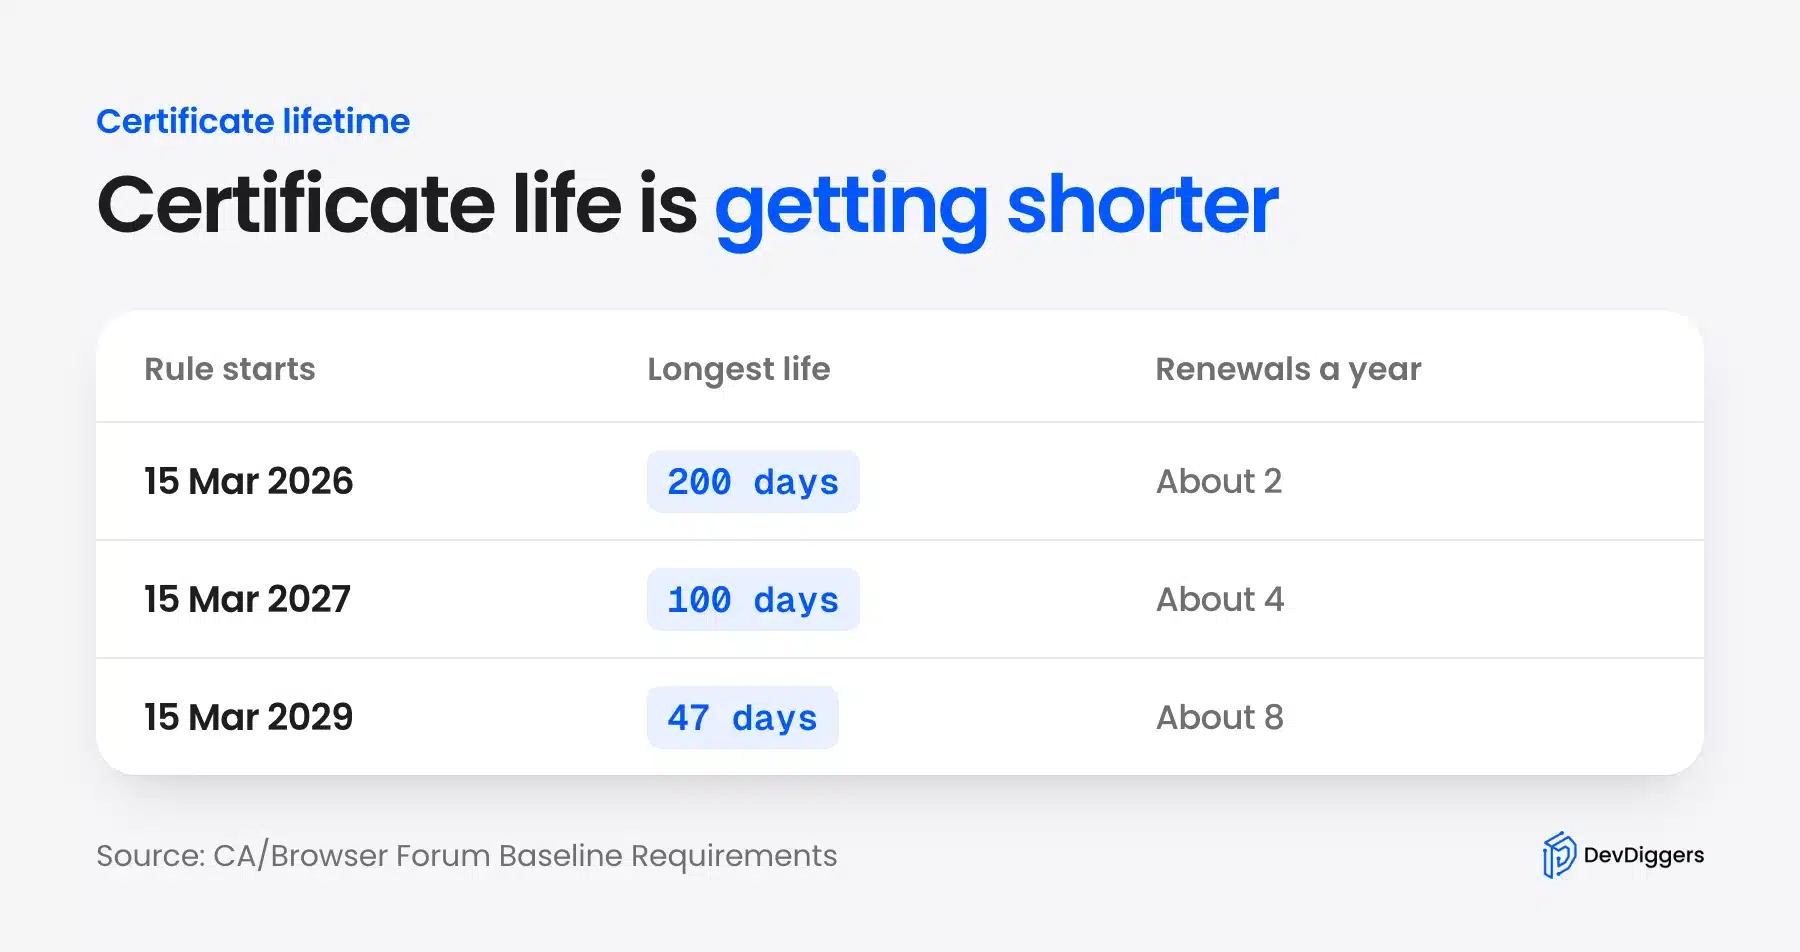
A public SSL certificate issued today can last at most 200 days. That limit started on March 15, 2026, and it drops to 100 days in 2027 and 47 days in 2029. Renewing by hand once a year no longer works when no certificate lasts a year.
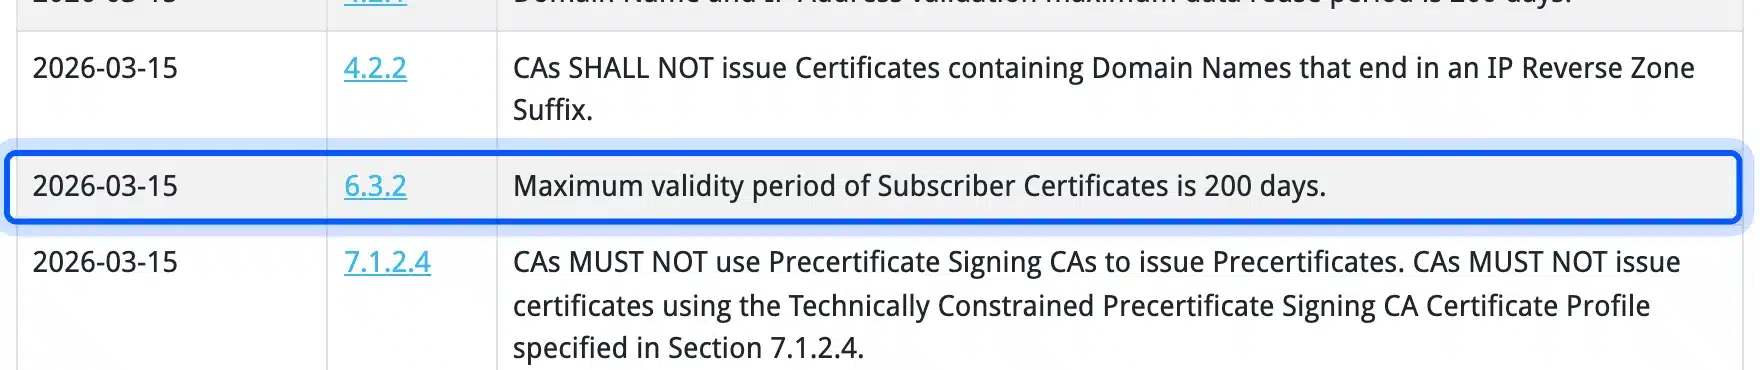
The CA/Browser Forum Baseline Requirements set these limits in their table of relevant dates. Version 2.3.1 of October 2026 lists 200 days from March 15, 2026, 100 days from March 15, 2027 and 47 days from March 15, 2029.
We wanted to see what this looks like on real sites. On October 27, 2026 we read the certificate served by 13 large websites, including Google, Amazon, WordPress.org and WooCommerce.com.
Not one of them served a certificate longer than 199 days. Ten of the 13 used certificates of 100 days or less, and most were 90 day certificates from Let’s Encrypt or Google Trust Services.
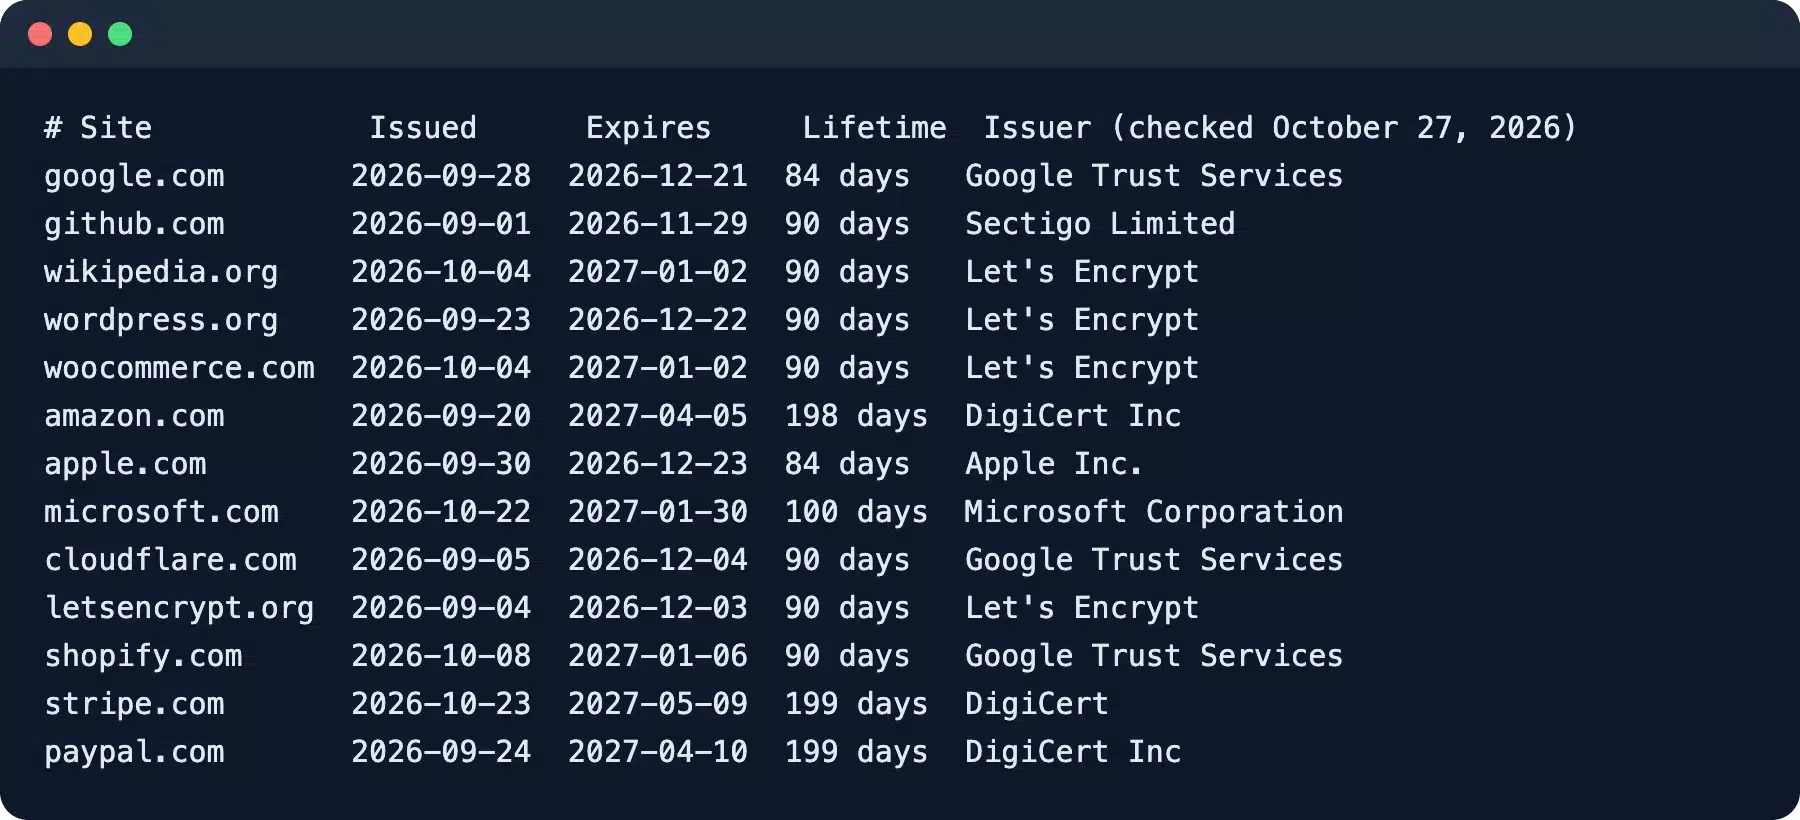
The three DigiCert certificates at Amazon, Stripe and PayPal sat at 198 or 199 days. That is the new ceiling, and those sites already renew about twice a year.
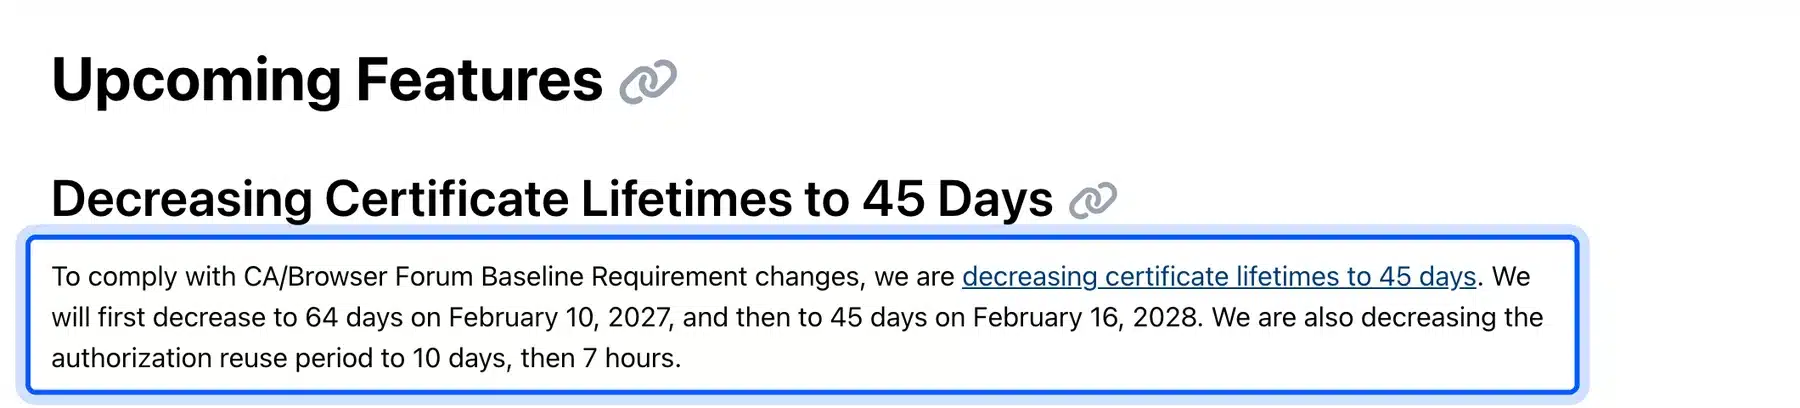
Let’s Encrypt is moving faster than the rules require. Its upcoming features page says default certificates drop to 64 days on February 10, 2027, and to 45 days on February 16, 2028.
Two older Let’s Encrypt changes also matter for renewals. It stopped sending expiration emails on June 4, 2025. Nobody warns you about a failed renewal anymore.
It also ended OCSP support and planned to switch its OCSP responders off on August 6, 2025. Your own monitoring now has to catch what the reminder email used to catch.
How to Run an SSL Certificate Expiry Check
The fastest SSL certificate expiry check is one openssl command that prints the start date, the end date and the issuer. It needs only your domain and works from any Mac or Linux terminal. The issuer line tells you who renews the certificate and so which method applies.
This command reads the certificate your site serves right now:
openssl s_client -connect example.com:443 -servername example.com </dev/null 2>/dev/null | openssl x509 -noout -dates -issuer
Replace example.com with your domain. The notAfter line is your SSL certificate expiration date.
We ran it against devdiggers.com on October 27, 2026. The certificate was issued on October 3, 2026 and expires on January 1, 2027. That is a 90 day life.
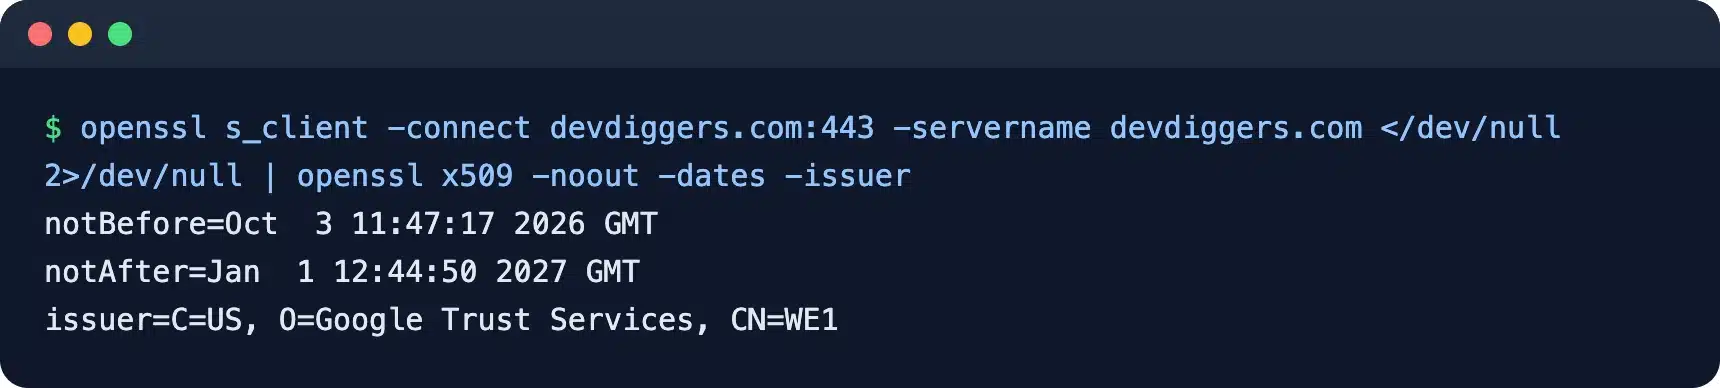
The issuer is Google Trust Services WE1. That tells us our CDN issues and renews the certificate. Method 1 covers that case.
You can also check in a browser. Chrome’s help page says to select the security icon to the left of the web address. That opens the site’s security summary, and the certificate details show the same dates.
To automate the check, use openssl’s checkend option. It exits with 0 when the certificate stays valid for the number of seconds you give. It exits with 1 when it does not.
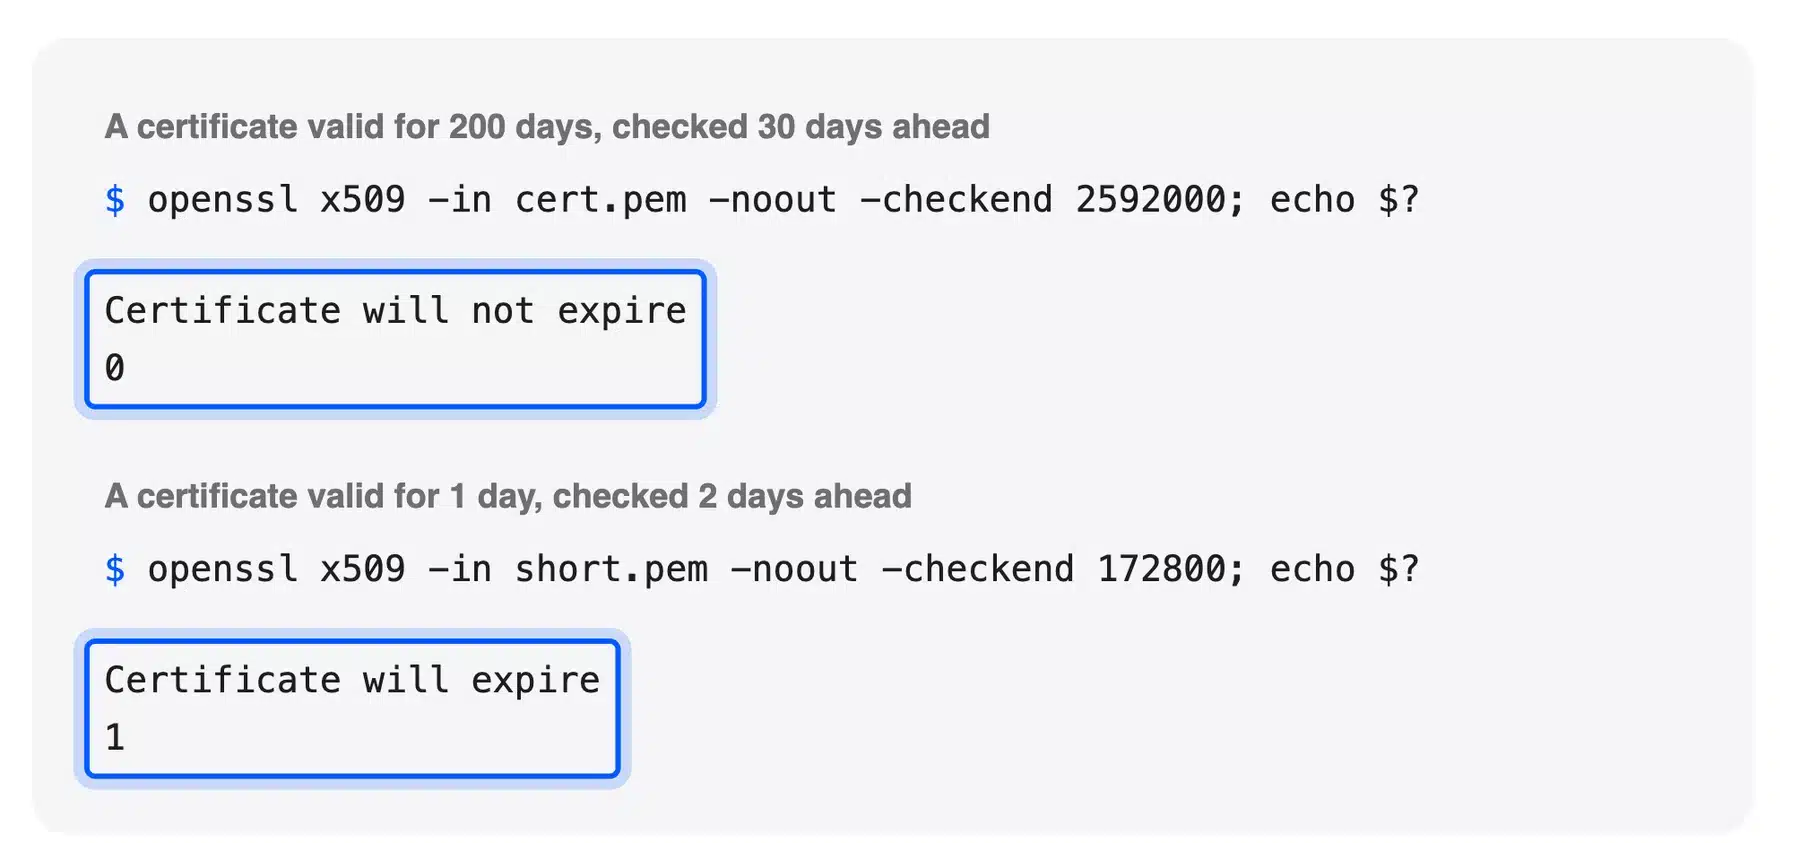
Put this in a daily cron job to get a warning 14 days before expiry:
openssl s_client -connect example.com:443 -servername example.com </dev/null 2>/dev/null | openssl x509 -noout -checkend 1209600 || echo "Certificate expires within 14 days"
The message prints only when the certificate ends within 14 days. Send that output to your email or a chat tool.
How to Renew SSL Certificate: Pick Your Method
How to renew SSL certificate coverage depends on who issued it. A free certificate from your host, your CDN or Let’s Encrypt renews itself when the setup works. A paid certificate from a commercial authority needs you to order the renewal and install the new files.
Read the issuer line from the expiry check. Find your case in this table:
| Issuer you see | Who renews it | Your method |
|---|---|---|
| Let’s Encrypt, Sectigo or cPanel on a shared host | Your host’s AutoSSL | Method 1 |
| Google Trust Services or Let’s Encrypt behind Cloudflare | Cloudflare Universal SSL | Method 1 |
| Let’s Encrypt on your own server | Certbot on that server | Method 2 |
| DigiCert, Sectigo or another paid brand you bought | You at the seller | Method 3 |
If the issuer surprises you, ask your host before you change anything. A certificate you did not buy is almost always one your host or CDN manages.
Method 1: Let Your Host or CDN Renew It
Most sites today auto renew SSL certificate coverage through their host or CDN with no commands. cPanel hosts use AutoSSL, and Cloudflare uses Universal SSL. Your job is to keep DNS pointing at the right place and to check the status page once a month.
In cPanel, open Security > SSL/TLS Status. cPanel’s documentation describes a filter called Has AutoSSL Problems. It lists every domain with a fault, such as a domain that does not resolve to an IPv4 address.
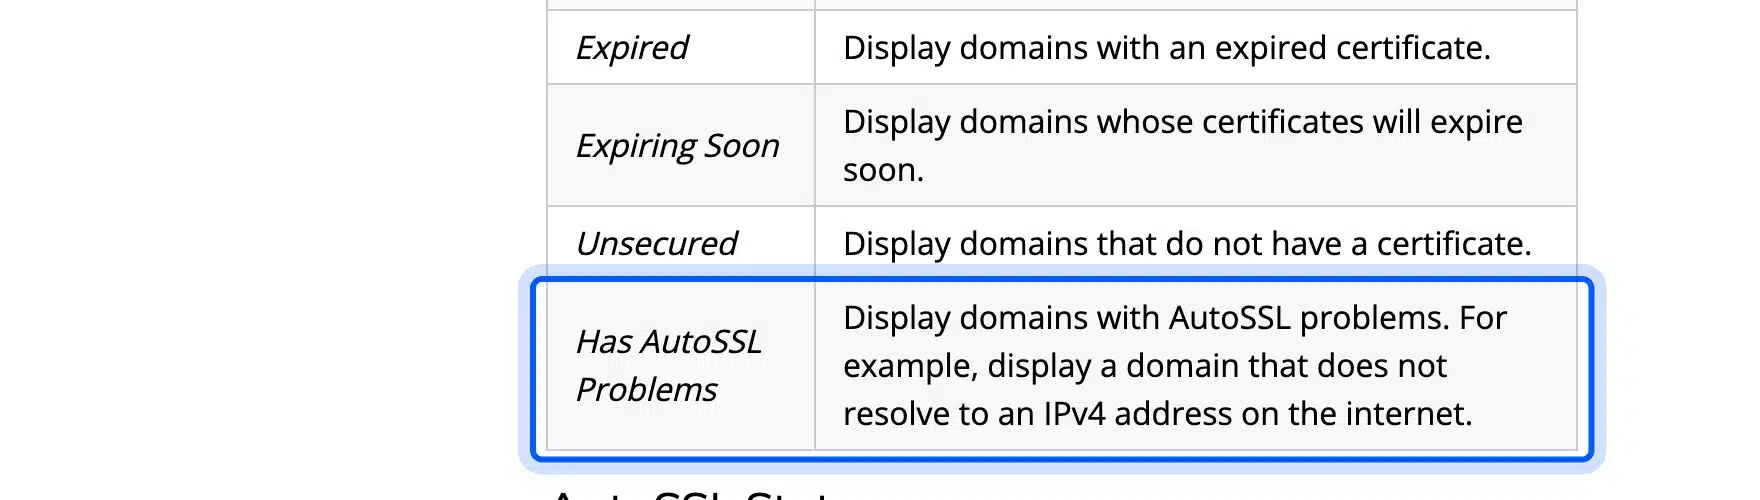
AutoSSL only covers domains on your hosting account. A domain whose DNS points to another server will not renew there. Fix the DNS first.
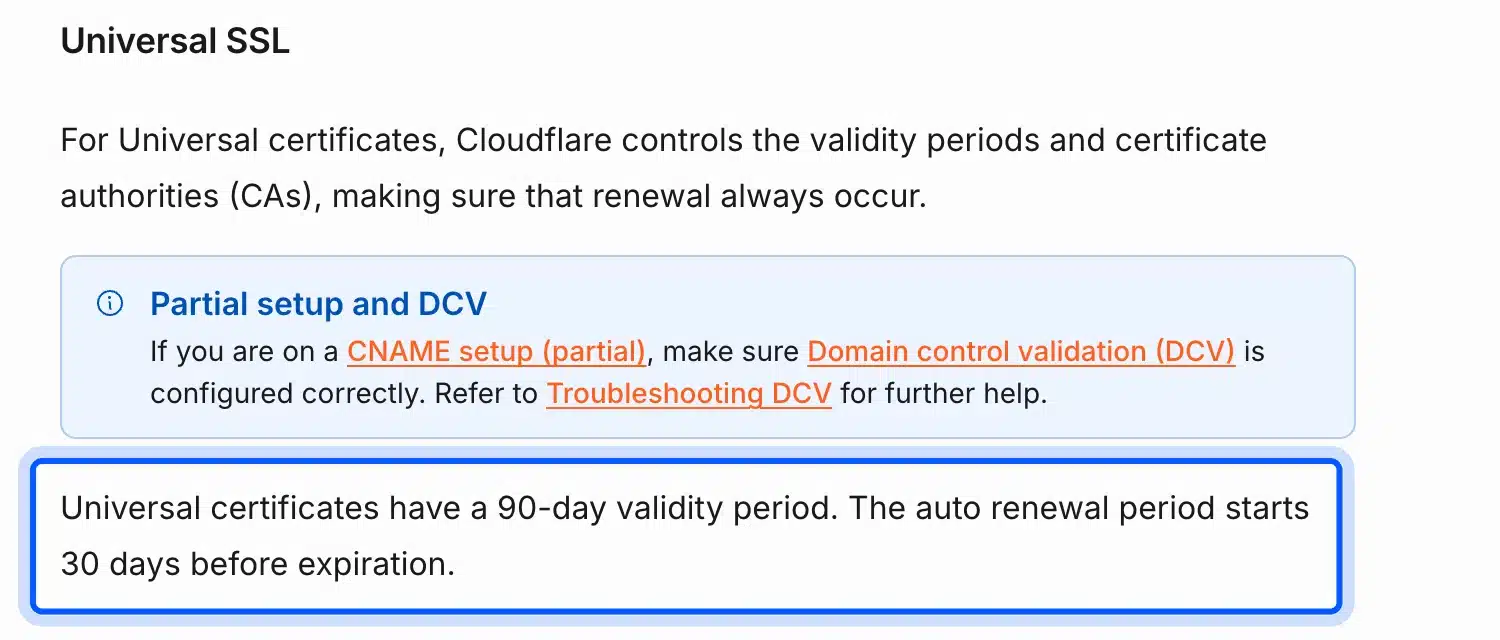
Cloudflare’s Universal SSL handles issuance, renewal and deployment on its own. Its validity periods page says Universal certificates last 90 days and renewal starts 30 days before expiry.
Our own site runs on Cloudflare. We checked whether that is what happens in practice. Every public certificate is logged in Certificate Transparency, and a free search on crt.sh lists them.
The Google Trust Services certificates for devdiggers.com were reissued every 59 or 60 days for a full year. Each renewal landed about 31 days before the old certificate expired. That matches the documented 30 day window.
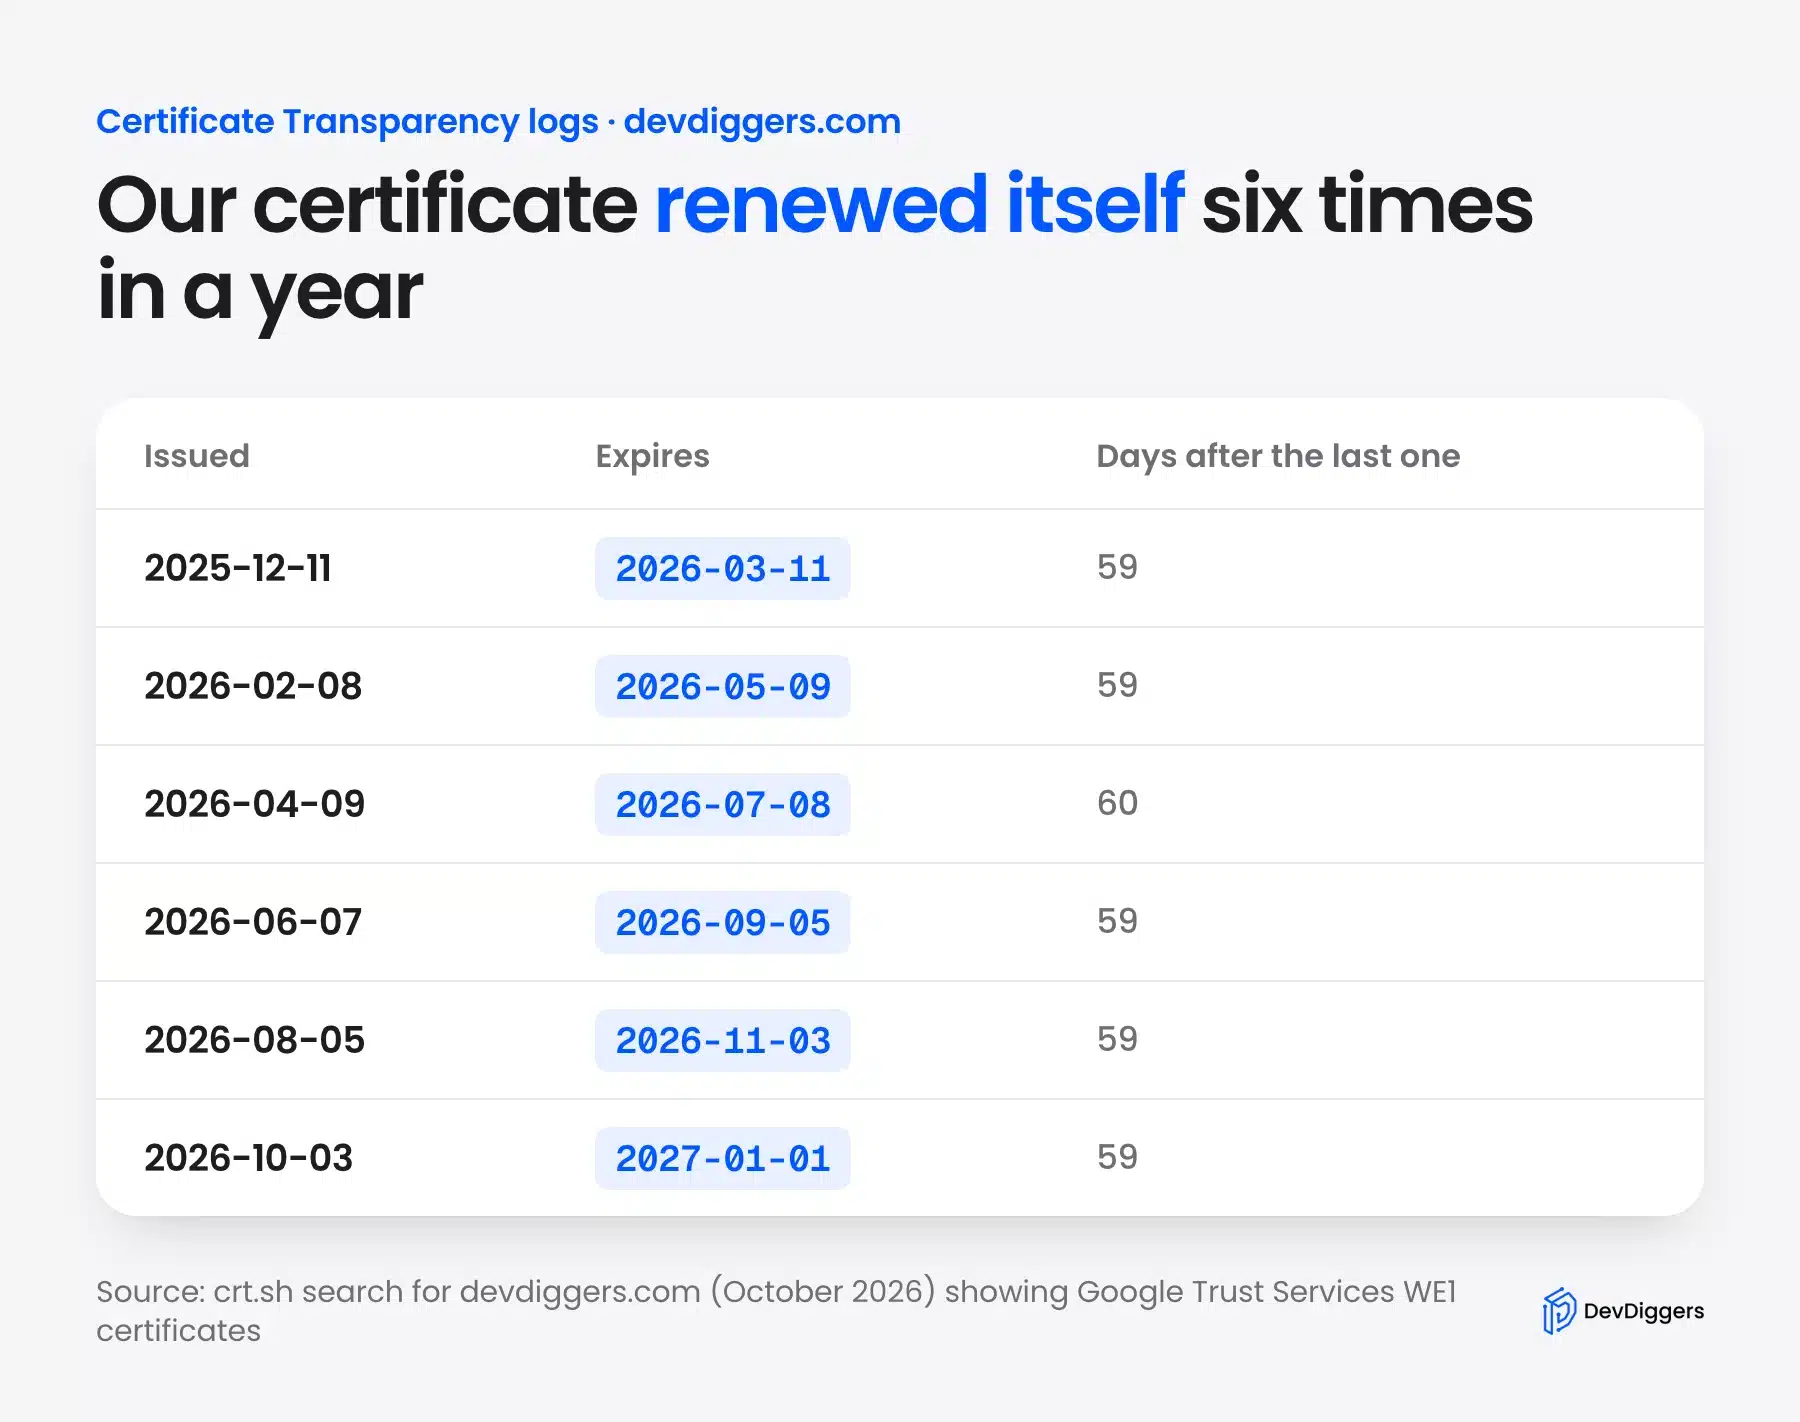
You can run the same search for your own domain. A steady pattern means renewal works, and a gap means it failed at least once.
Method 2: Let Certbot Renew It
Certbot is the usual ACME client for Let’s Encrypt certificates on a server you manage yourself. Its renew command checks every installed certificate and renews only those that are due. Running it twice a day is safe because it does nothing until a certificate nears expiry.
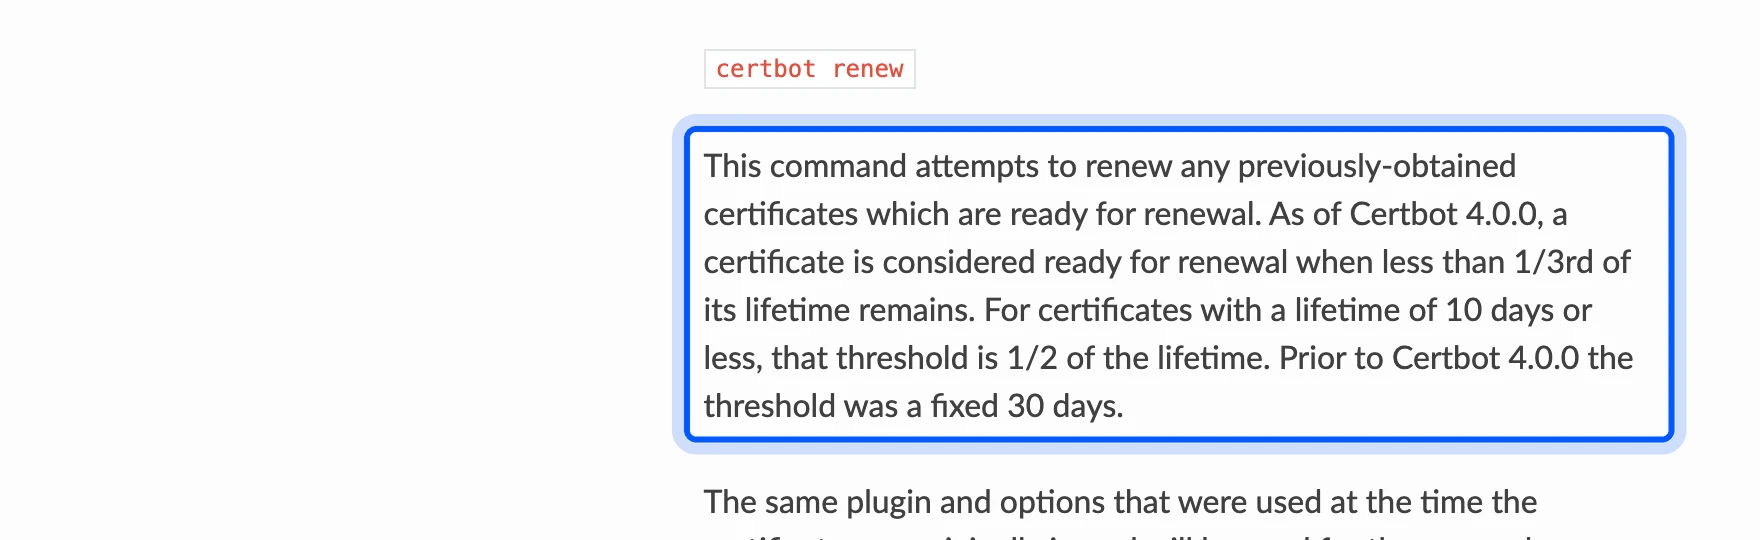
Certbot’s documentation says a certificate is ready for renewal when less than one third of its lifetime remains. For a 90 day certificate that means about 30 days before expiry.
Many install methods add a systemd timer or a cron job for you. Certbot’s docs suggest checking for an existing timer before adding your own line. Then test the whole setup with a dry run:
sudo certbot renew --dry-run
The docs say a dry run performs a test against the Let’s Encrypt staging server and gets test certificates. Your live certificate stays untouched.
Let’s Encrypt’s FAQ gives the same timing for its 90 day certificates, with renewal every 60 days.
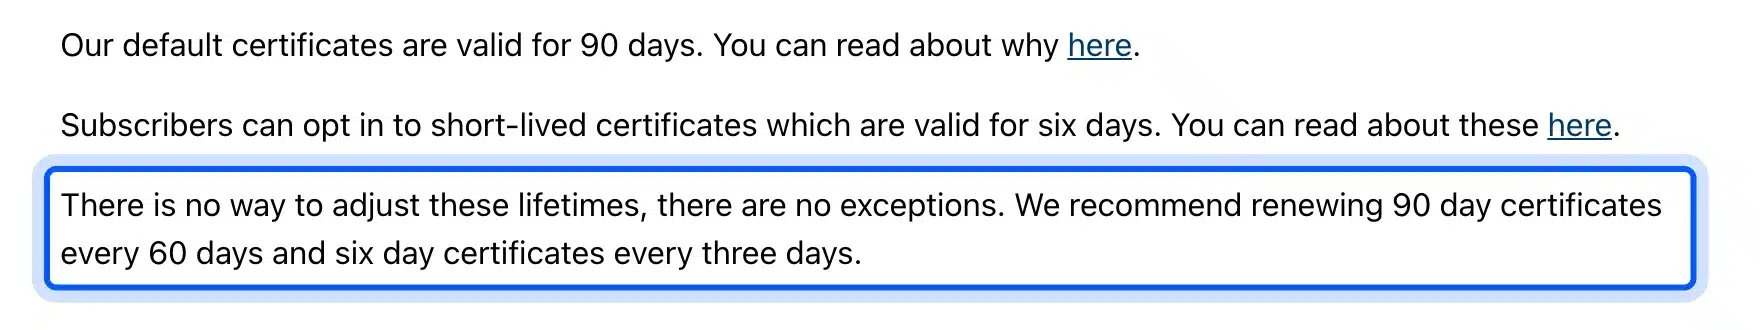
Let’s Encrypt’s announcement says users who issue certificates automatically will not have to make any changes for the shorter lifetimes. A hard-coded “renew every 60 days” rule is the one setup that will break.
Add a deploy hook if your web server must reload after a renewal. Certbot runs the --deploy-hook command once for each certificate it renews.
We left Certbot out of our own tests. A dry run requests a real staging certificate, and that needs a public domain pointing at the server.
Method 3: Renew a Paid Certificate by Hand
A manual SSL certificate renewal still applies to certificates you bought from a commercial authority. The pattern is the same at most sellers. You order the renewal, create a new CSR, prove you control the domain and install the new files on your server.
Gandi’s documentation is a clear example. You can renew up to 30 days before expiry. A renewal needs a new CSR because the old CSR and private key cannot be reused.
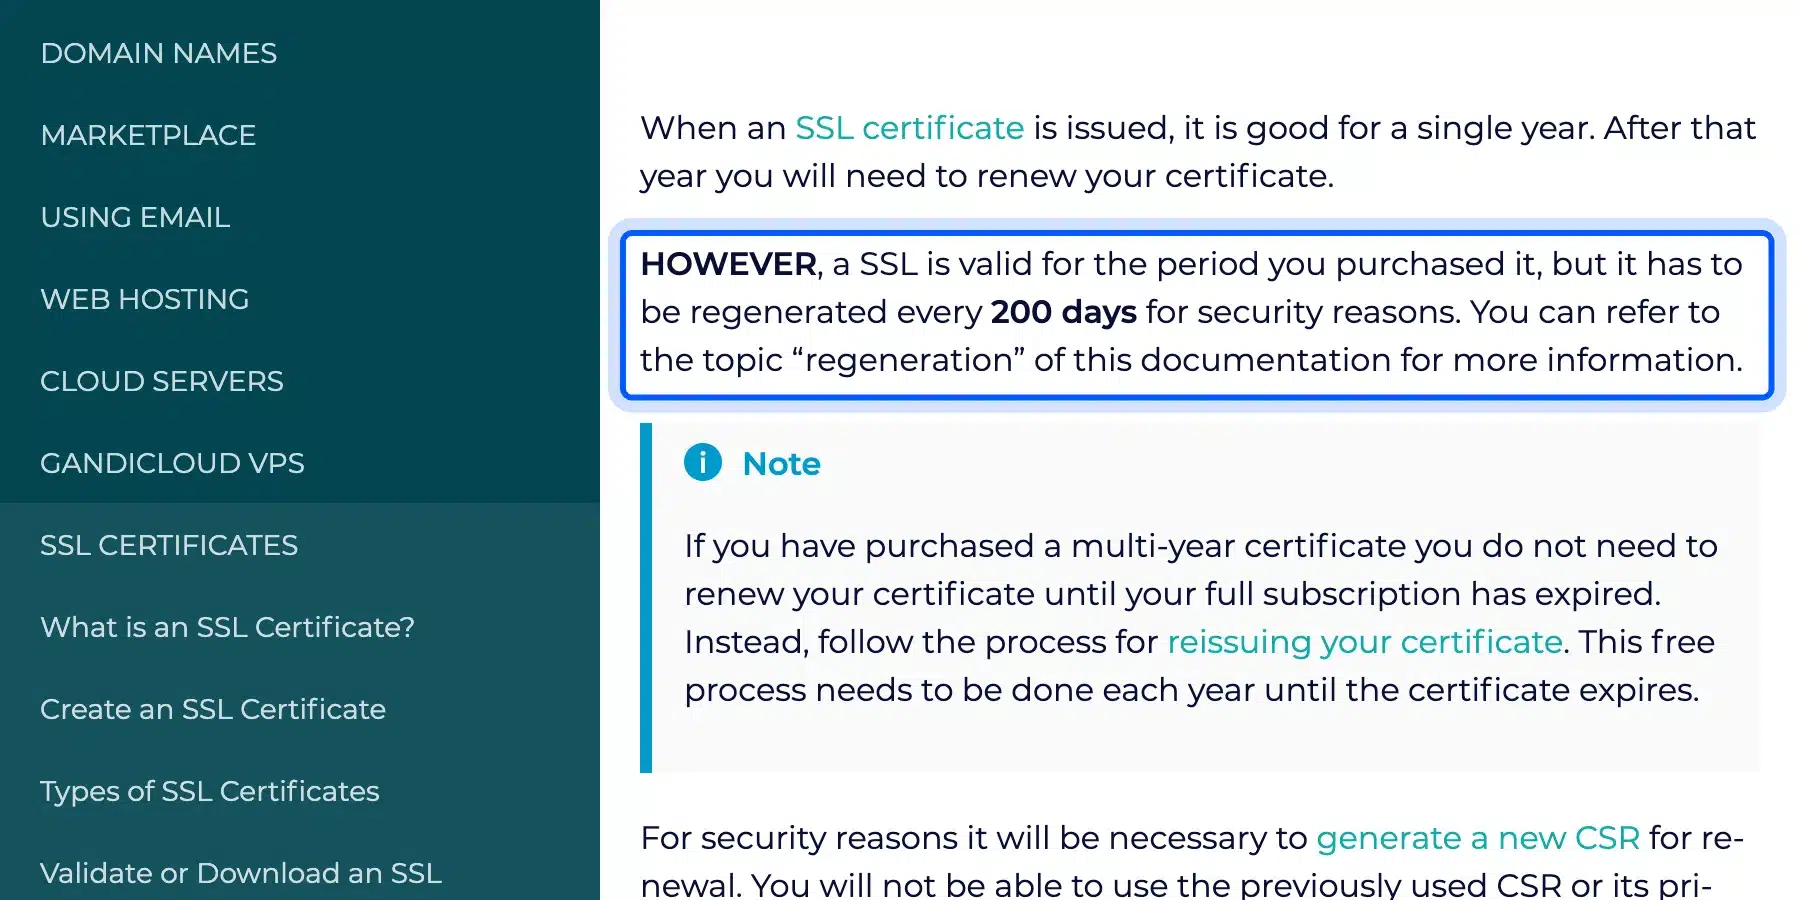
Gandi also states that a certificate must be regenerated every 200 days. A multi-year plan now means you reissue the certificate inside your subscription, about twice a year.
Here is the order that works for most accounts:
- Start the renewal: Use the renewal button or email from your seller.
- Create a new CSR: Your host or server software generates it together with a new private key.
- Validate the domain: Add the DNS record or click the email link your seller asks for.
- Install the new files: Upload the certificate and the chain. Reload the web server after that.
- Check the result: Run the openssl command from earlier and read the new notAfter date.
Validation also expires sooner now. The same Baseline Requirements cut domain validation reuse to 200 days in 2026 and 10 days in 2029. A DNS record method you can repeat beats an email link that someone has to click.
Namecheap’s renewal guide adds a warning for business certificates. OV and EV renewals may need company re-validation. Start those early.
Does an EV Certificate Still Show Your Company Name?
No. Chrome stopped showing the company name for EV certificates in the address bar in Chrome 77. The Chromium team moved that information to the Page Info panel behind the icon next to the address.
Pay for an EV certificate only when your business needs its validation for a contract or an audit. Visitors no longer see a difference.
What to Check in WordPress After You Renew
A renewed certificate does not fix a WordPress site that still loads files over plain HTTP. After every renewal or certificate change, confirm that Site Health sees HTTPS and that both site URLs use it. Then clear mixed content and caches, and know what your HSTS header does.
We ran these checks on our WordPress 7.1.3 and WooCommerce 11.2 test site, and on our live site where that was safe. Each step below shows the real screen or the real output.
Purge every cache layer after a certificate change. That means your page cache plugin, your host’s cache and your CDN, since each can keep serving pages built with old addresses. Our roundup of WordPress caching plugins shows where each one keeps its purge button.
Confirm Site Health Sees HTTPS
WordPress checks HTTPS itself. The WordPress 5.7 developer note says a cron job runs twice a day to test whether the site works over HTTPS. Site Health reports a failed test as a critical issue.
Open Tools > Site Health. Our test site runs without HTTPS. It shows the warning you want to see gone after renewing.
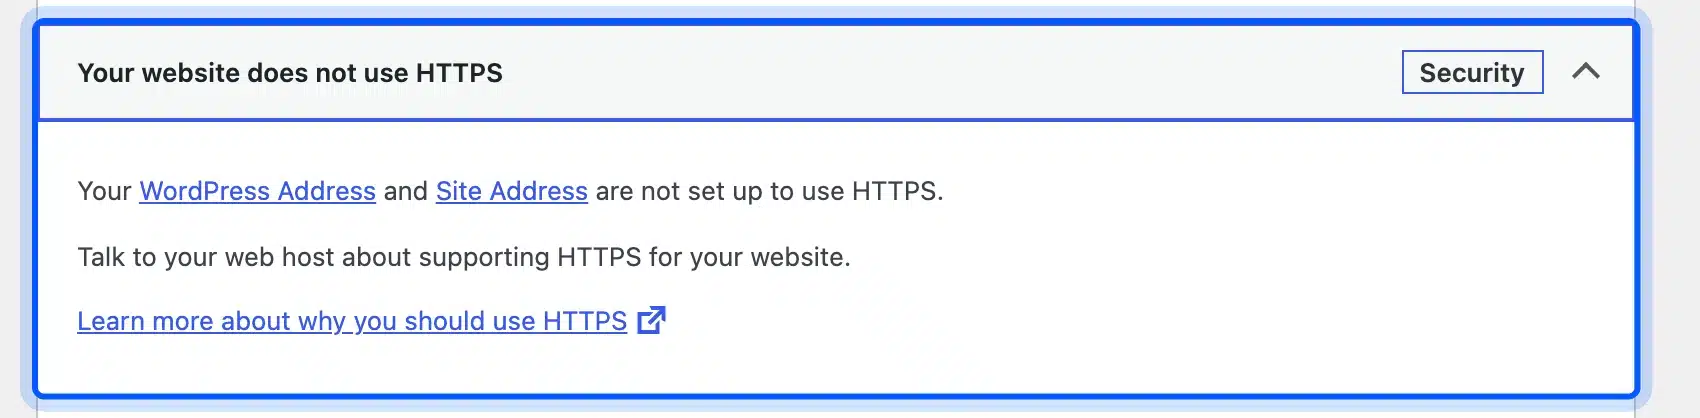
On a WooCommerce store, Site Health also lists “WooCommerce store is not using a secure connection” as a critical issue. Both items should disappear once HTTPS works.
Set Both URLs to HTTPS
Go to Settings > General and check the WordPress Address and Site Address fields. Both must start with https:// and match the domain on your certificate.
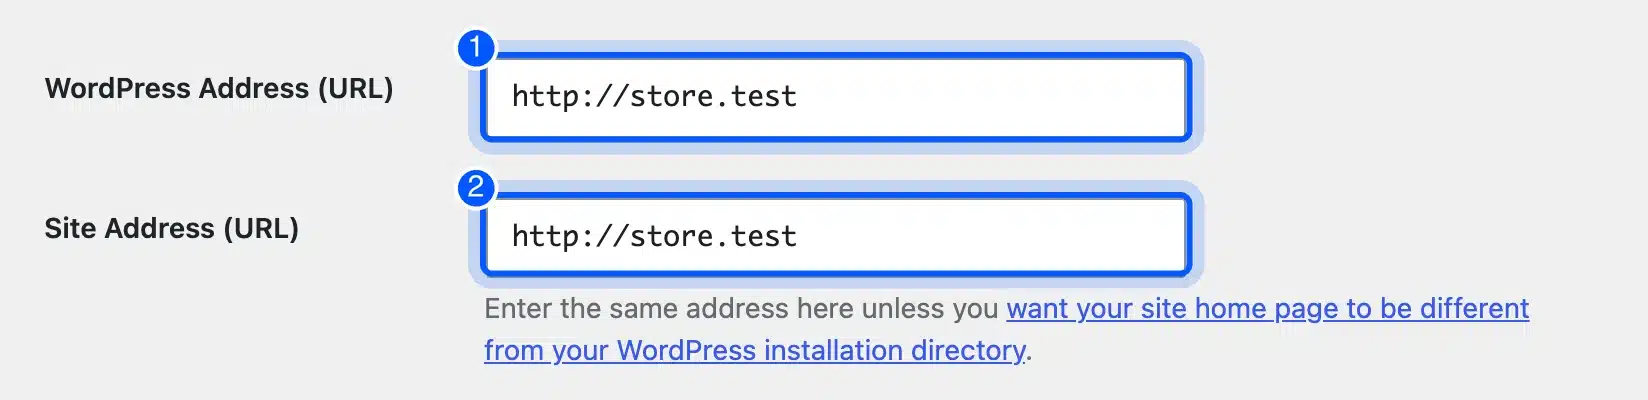
Change them only once the certificate works, or you can lock yourself out of the dashboard. The WordPress HTTPS guide also recommends FORCE_SSL_ADMIN in wp-config.php for admin sessions. If the site then loops between HTTP and HTTPS, our guide to the ERR_TOO_MANY_REDIRECTS error walks through the fix.
Fix Mixed Content
Mixed content is an HTTPS page that still loads files over HTTP. MDN’s mixed content page says browsers auto-upgrade images, video and audio and block other insecure requests.
We tested this in Chrome 156 with an HTTPS page that requested one image, one script and one stylesheet over HTTP. Chrome upgraded the image to HTTPS and blocked the script and the stylesheet.
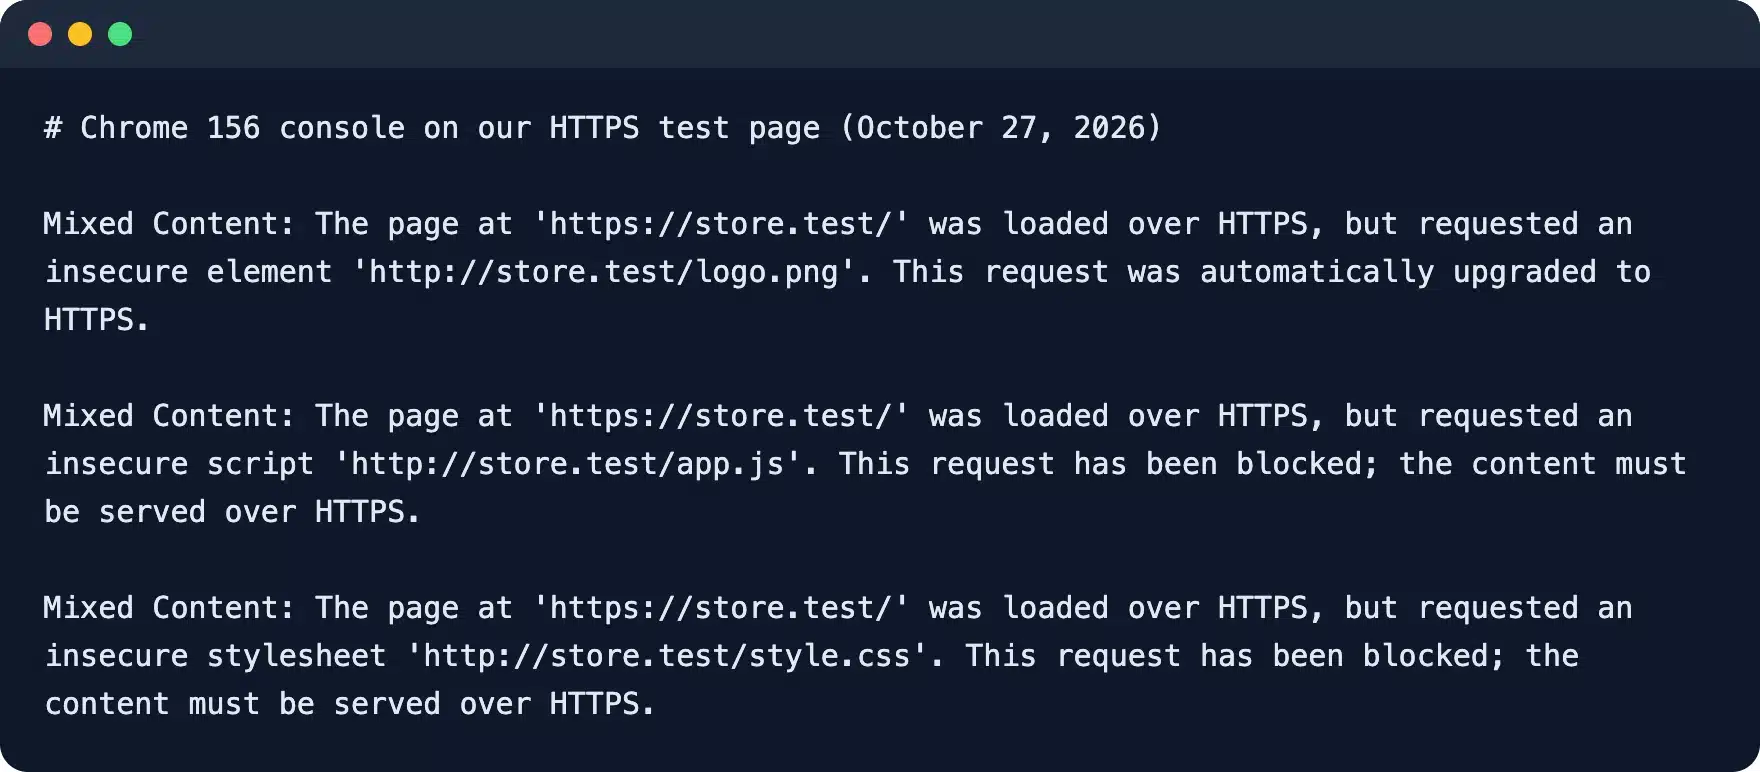
So a broken layout or a dead button after the switch usually points to a theme or plugin file still linked over HTTP. Open the browser console on the page and look for Mixed Content lines.
WordPress 5.7 also replaces insecure URLs in post content on the fly after a one-click switch from Site Health. Hard-coded files in a theme or a plugin are not covered by that.
Check Your HSTS Header
HSTS tells browsers to use only HTTPS for your domain. Run this command to see whether your site sends it:
curl -sI https://example.com/ | grep -i strict-transport-security
Our site sends a one year policy that covers subdomains.
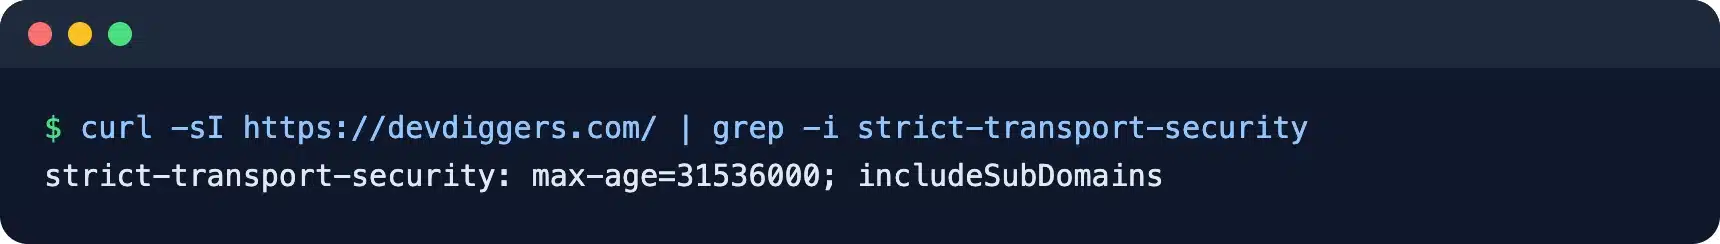
That raises the stakes of a failed renewal. MDN’s HSTS reference says that on an HSTS host, the browser gives visitors no way to click through a certificate error.
How Long Does an SSL Certificate Take to Update?
A renewed certificate takes effect as soon as the web server loads it, usually within seconds of a reload. Most of the wait is validation and issuance at the authority. An old certificate that still shows means a server, a proxy or a CDN is serving it.
The timing has three parts. Domain validation by DNS can wait on your DNS record to appear. Issuance by an ACME authority such as Let’s Encrypt usually finishes within minutes.
Installation is instant once the server reloads. Visitors get the new certificate on their next new connection. Ask them to close and reopen the tab if they still see a warning.
If you renewed and the openssl check still shows the old notAfter date, check three places. First, confirm the server reloaded.
Next, check whether a CDN or load balancer holds its own copy. Last, confirm the files landed on the right server.
On Cloudflare, Universal certificates are issued after your domain is active on Cloudflare, according to its Universal SSL page. Your origin certificate is separate, and you renew it on your own server.
How to Fix a Failed SSL Auto-Renewal
Fix a failed auto-renewal by reading the error first. Check the renewal log, confirm your domain points to the server that requested the certificate, and run the renewal again by hand. Then confirm the new expiry date with the openssl command.
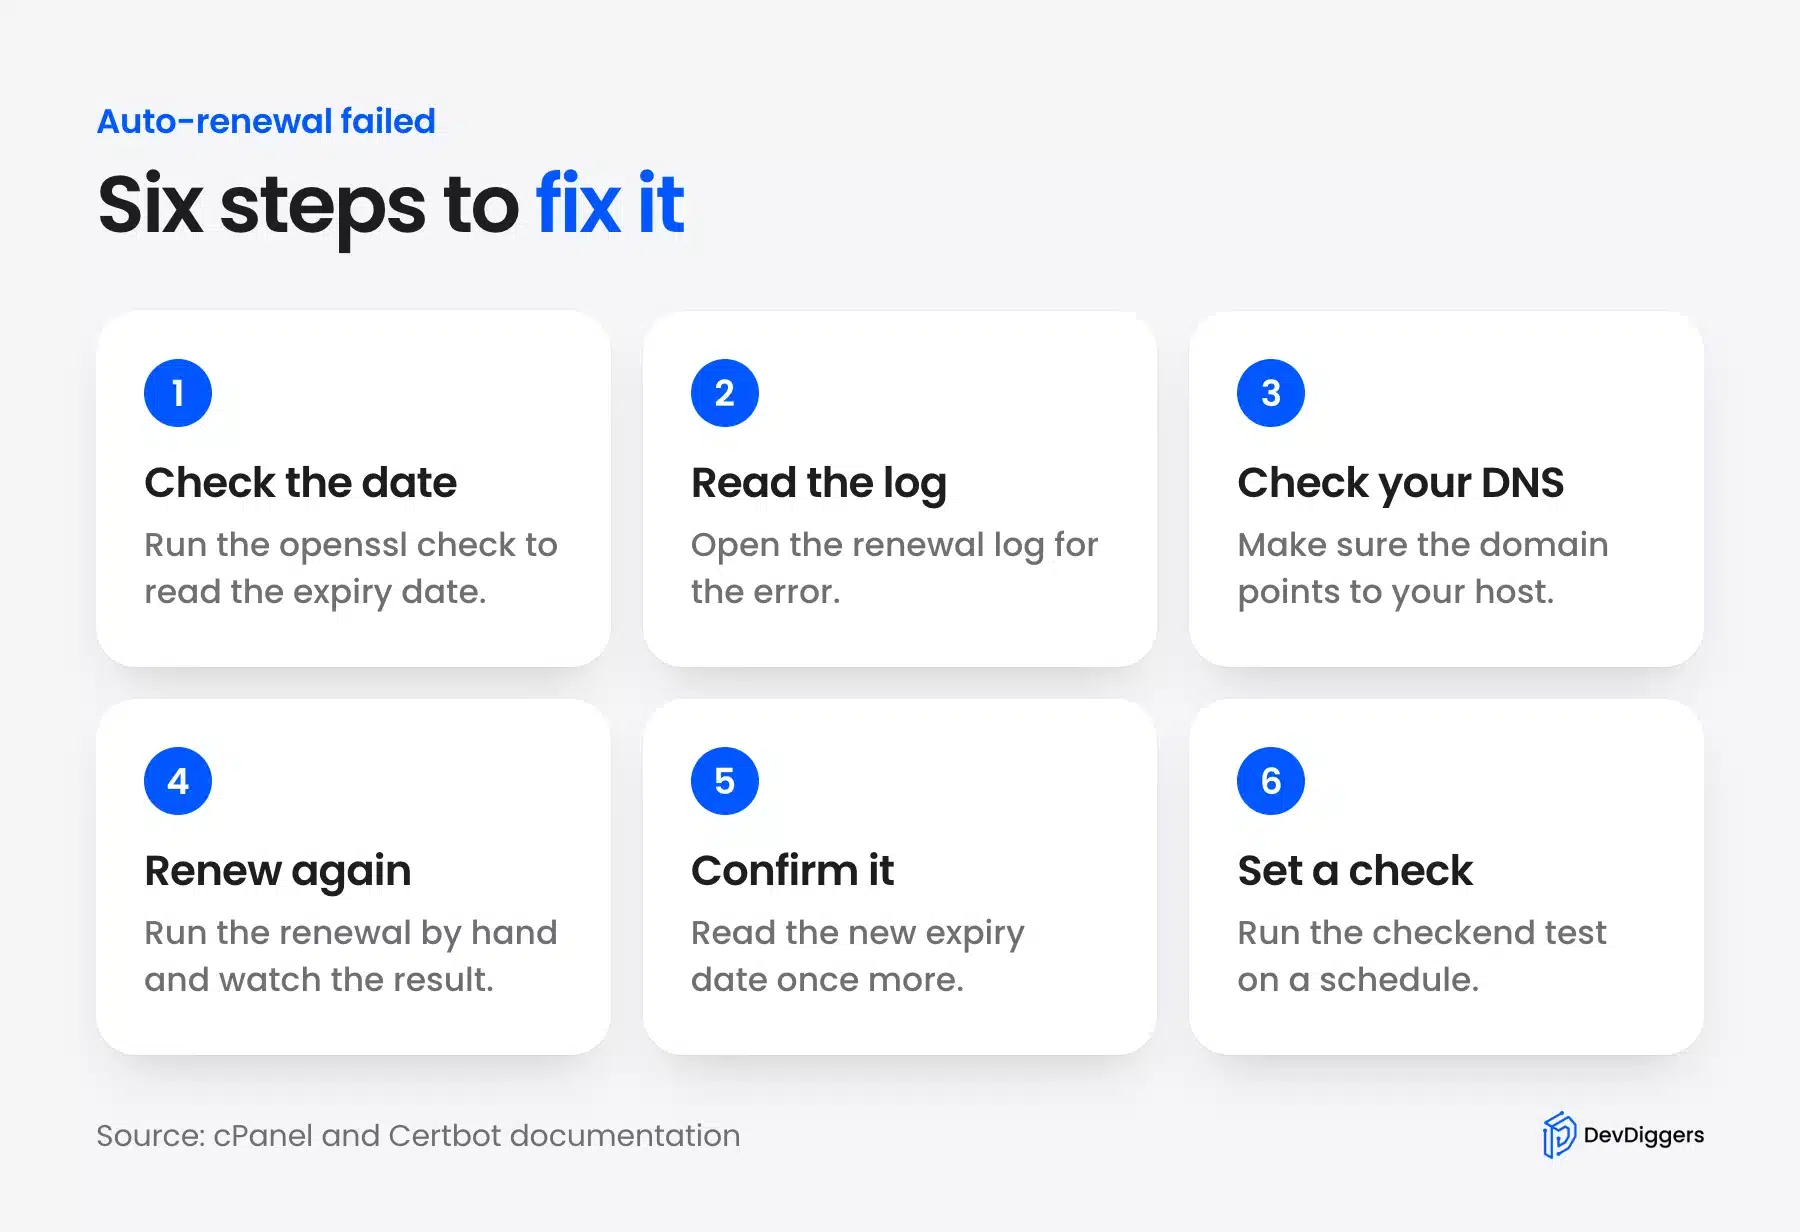
In cPanel, AutoSSL errors are written to /var/cpanel/logs/autossl/, according to the cPanel page linked in Method 1. Certbot prints its error to the terminal when you run sudo certbot renew by hand.
DNS is the most common cause after a move. Your A record must point to the server that answers the validation request.
After the fix, run the renewal once and wait for the next AutoSSL run, or ask your host to start one. Then run the expiry check and note the new date.
Keep the checkend cron job from the expiry section running. Let’s Encrypt no longer emails you before expiry. That job is now your warning system.
For a WordPress site, our WordPress security checklist lists the other items worth watching on the same schedule.
What Happens When an SSL Certificate Expires?
When an SSL certificate has expired, browsers show a full-page warning such as “Your connection is not private”. Most visitors leave at that point. On a site with HSTS, the browser does not even offer a way past the warning.
Chrome’s help page says this error can come from the site, the network or the device. If many visitors see it at once, the site is the cause.
You cannot extend an expired certificate. You get a new one through the method that matches your issuer. Install it and reload the server.
With an SSL certificate expired on an HSTS site like ours, every visitor is locked out until the new one is live. That is why the daily check matters more than the renewal itself.
Our guide on fixing common SSL issues in WordPress covers the other certificate errors. The ERR_SSL_PROTOCOL_ERROR message is a different fault that looks similar.
Some store owners would rather hand this off. A WordPress maintenance service can watch certificate dates and renewals for you. That helps when one failed renewal would cost sales.
Conclusion
The answer to how to renew SSL certificate coverage in 2026 is to automate it and verify it. Let your host, Cloudflare or Certbot renew free certificates, and keep manual renewal for the paid ones you bought.
Certificates already run 90 to 199 days on the large sites we checked. With 100 days due in 2027 and Let’s Encrypt at 64 days, a yearly reminder will not work.
Run the openssl check on your domain today and write down the notAfter date. Then add the daily checkend job and confirm Site Health shows no HTTPS issue.
Frequently Asked Questions (FAQs)
Q1. How often do SSL certificates need to be renewed?
A public certificate can last at most 200 days since March 15, 2026. The limit falls to 100 days in 2027 and 47 days in 2029. Let’s Encrypt and Cloudflare certificates last 90 days and renew about every 60.
Q2. Can I renew an SSL certificate before it expires?
Yes. Gandi lets you renew up to 30 days before the expiry date, and automated tools renew about 30 days early by default. Renewing early prevents a gap between the old and new certificate.
Q3. Do I need to renew a Let’s Encrypt certificate by hand?
No. Let’s Encrypt recommends renewal through an ACME client such as Certbot, and Certbot renews certificates with under a third of their life left. Test the setup once with sudo certbot renew --dry-run.
Q4. Does a renewal need a new CSR?
At Gandi it does, and its documentation says the old CSR and private key cannot be reused. Other sellers set their own rules on their renewal pages. A new key with each renewal is the safer habit anyway.
Q5. How do I extend a certificate’s expiration date?
You cannot extend an issued certificate. Its dates are fixed when the authority signs it. You get a new certificate with a new notAfter date and install it in place of the old one.
Q6. Can I do a certificate renewal online?
Yes. Paid renewals start in your seller’s online dashboard, and free ones renew online through your host or CDN. You still need to install the new files on your server unless your host does that step.
Q7. What does the 47 day limit mean for my site?
From March 15, 2029 the longest certificate life is 47 days. That is about eight renewals a year, and only automation keeps up with that pace. Sites already on Let’s Encrypt or Cloudflare should see no change.
Q8. Do OV and EV certificates renew differently?
They may need company re-validation on top of domain validation. Namecheap’s guide warns about this for OV and EV renewals. Start the renewal about a month early so paperwork does not delay the new certificate.