

You can limit login attempts in WordPress with a security plugin or a short PHP snippet. Either one takes about ten minutes to set up, and WordPress core does not count failed logins on its own.
We tested each method on a WordPress 7.1.3 test site in October 2026. We also tried a popular .htaccess counter rule, and it blocked every visitor from the first request.
This guide shows the plugin route and the code route. Next come the server options, Cloudflare and a CAPTCHA layer. It ends with a lockout test and the steps to get back in if you lock yourself out.
Does WordPress Limit Login Attempts by Default?
No, WordPress does not limit login attempts by default. The official brute force guide on WordPress.org treats a limiter as something you add through a plugin or a server rule. On our test site, six wrong passwords in a row all received the same ordinary error.
Nothing slowed down and nothing locked. The login screen printed the same error each time. The guessing could go on for as long as someone liked.
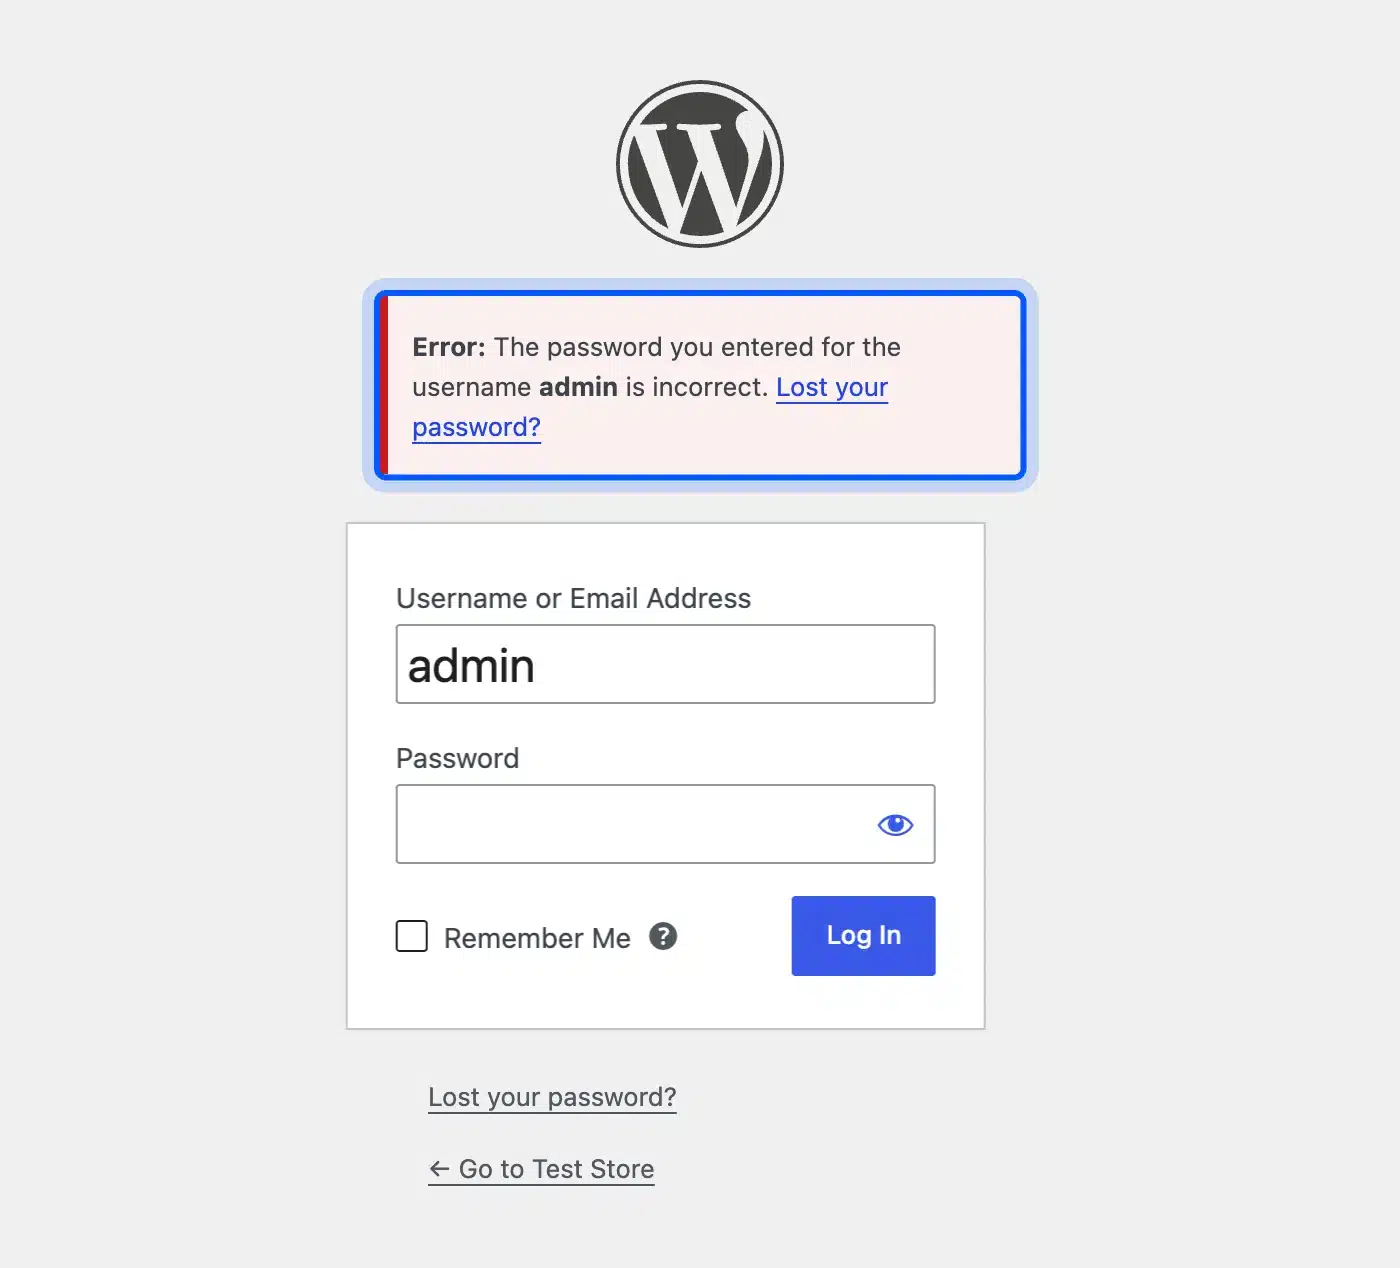
The default error also gave away more than it should. When we typed a real username, the message named that username and called its password incorrect. That confirms the account exists.
The same guide calls xmlrpc.php a frequent brute force target, especially its system.multicall method. It advises you to disable XML-RPC if you do not use it, and to restrict it if you do.
What Can Really Limit Login Attempts?
Only a tool that counts failed logins can limit login attempts. A security plugin, a short PHP snippet, a Cloudflare rule and fail2ban can all do that job. An .htaccess file cannot count failed logins and can only allow or block.
That last point matters because many older guides show an .htaccess “login counter”. The WordPress.org guide says older advice often recommended heavy .htaccess rewrites, and it calls such measures unreliable. We test one of those rules below.
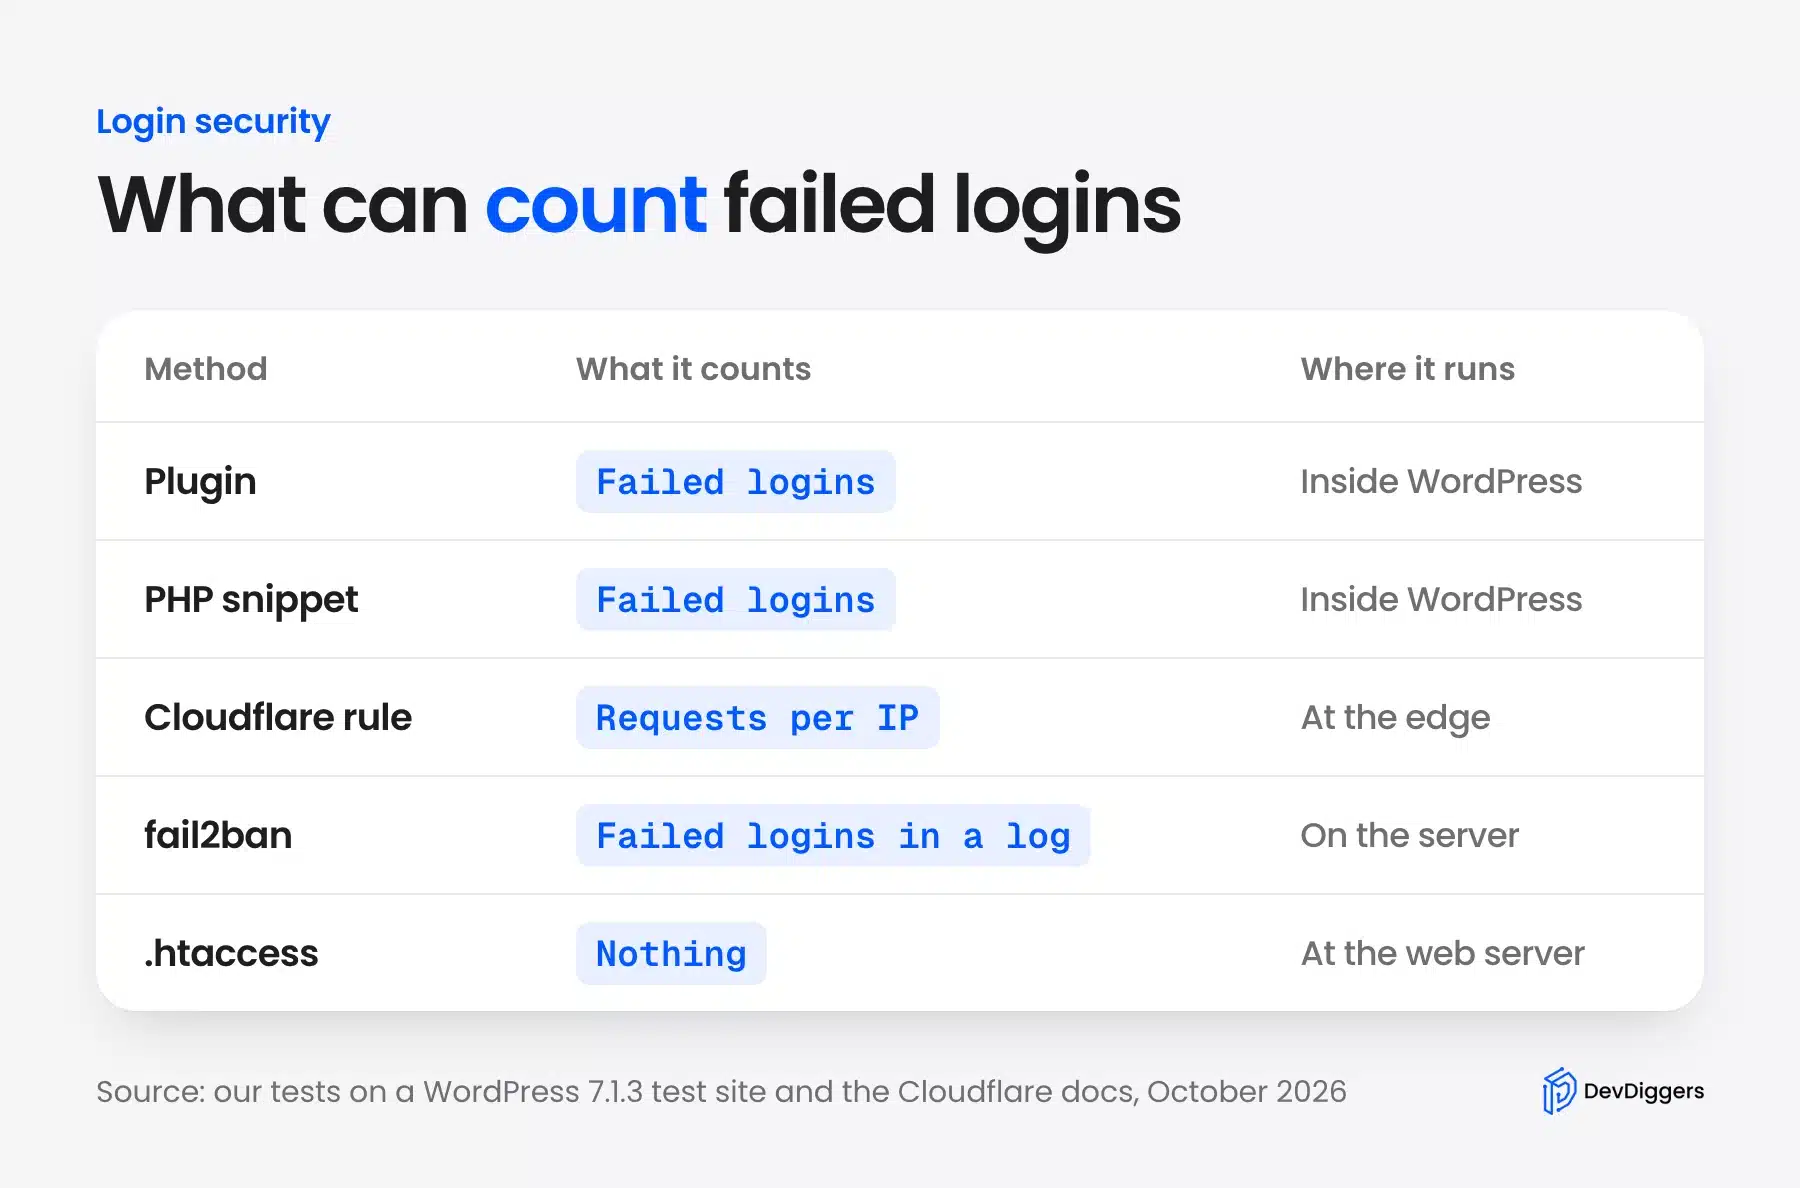
Each method lives in a different place. A plugin or snippet runs inside WordPress and every blocked request still loads PHP. The same guide prefers limits at the edge or the web server.
It warns that a plugin still uses PHP resources during heavy attacks. For a small site that is rarely a problem, but a busy login page can feel it.
For most sites the plugin is the right start. It needs no code, and it adds email alerts. Add an edge rule later if the login page ever gets enough traffic to slow your server.
Method 1: Limit Login Attempts in WordPress With a Plugin
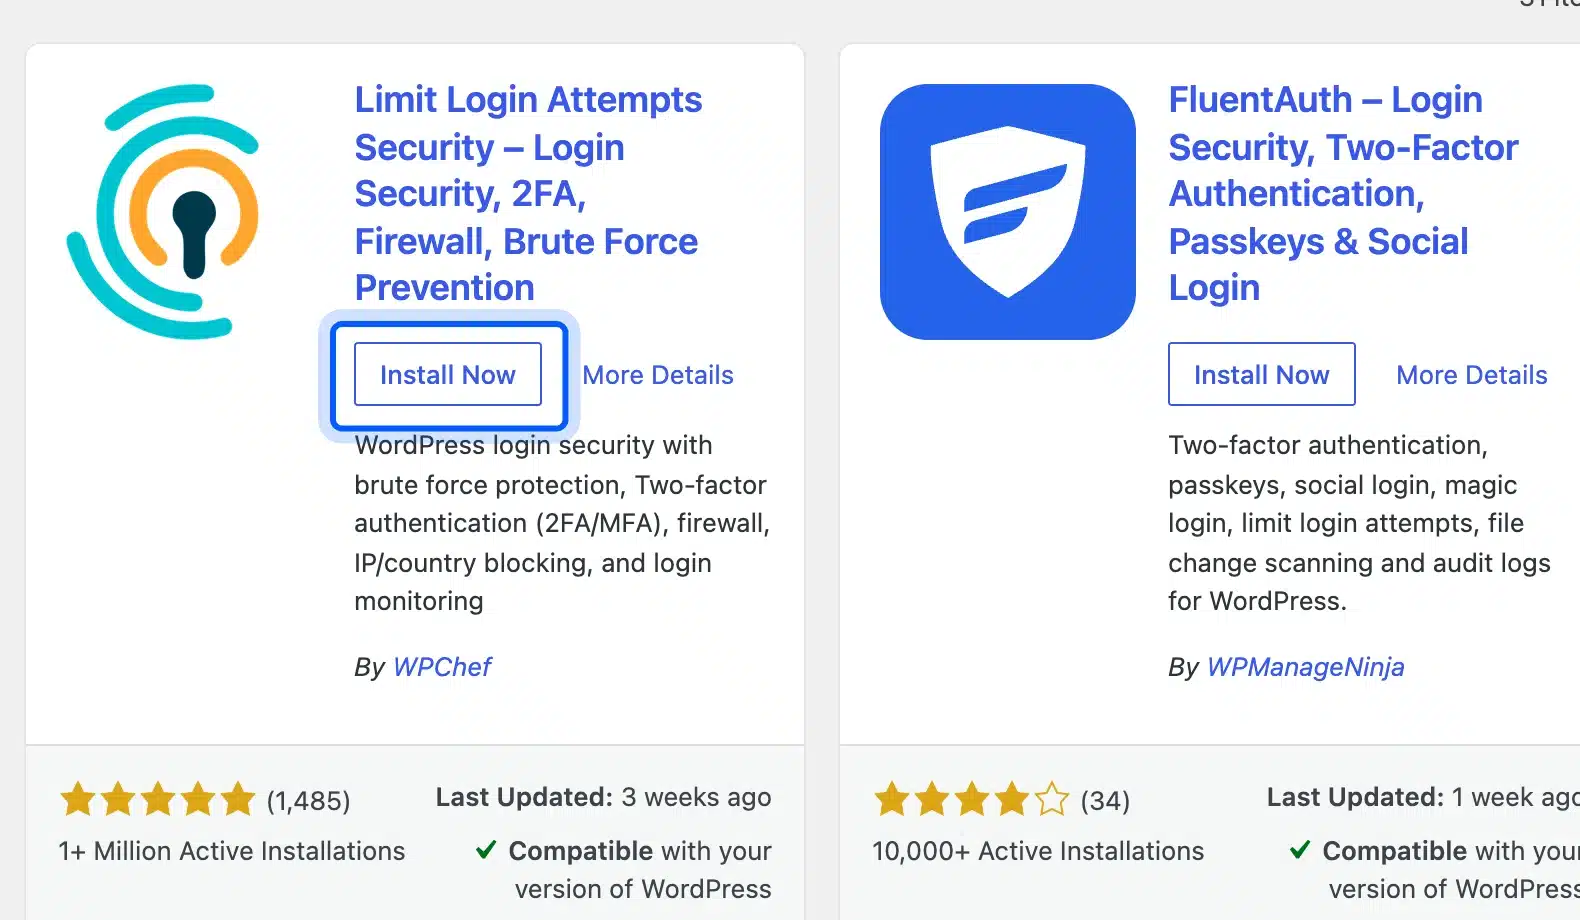
The fastest way to limit login attempts in WordPress is the Limit Login Attempts Reloaded plugin. Install it, and the default limits start working at once. The plugin page on WordPress.org lists more than 1 million active installations as of October 2026.
We used version 3.3.10 on WordPress 7.1.3. Several other security plugins also limit logins, including Wordfence and Loginizer. We tested only this one.
- Install the plugin: Go to Plugins > Add Plugin and search for “Limit Login Attempts Reloaded”. Click Install Now and Activate. The directory now lists it as Limit Login Attempts Security.
- Open the Settings tab: After activation, a short onboarding window opens first. It walks through notifications and a premium offer. When it closes, go to Limit Login Attempts > Settings.
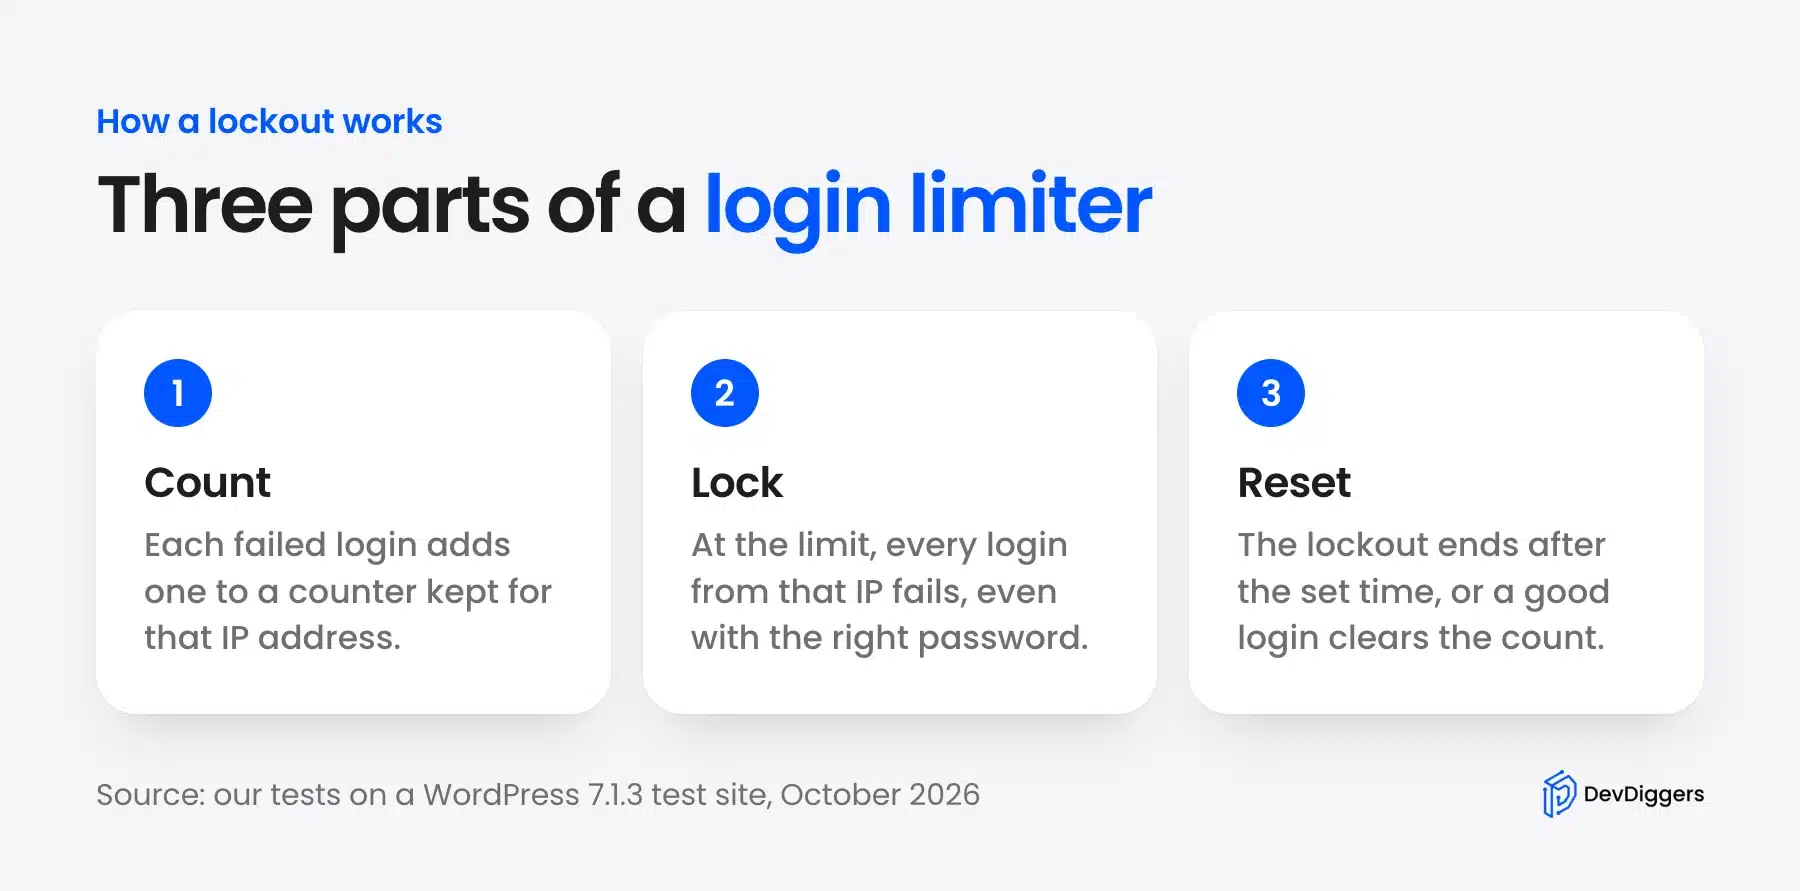
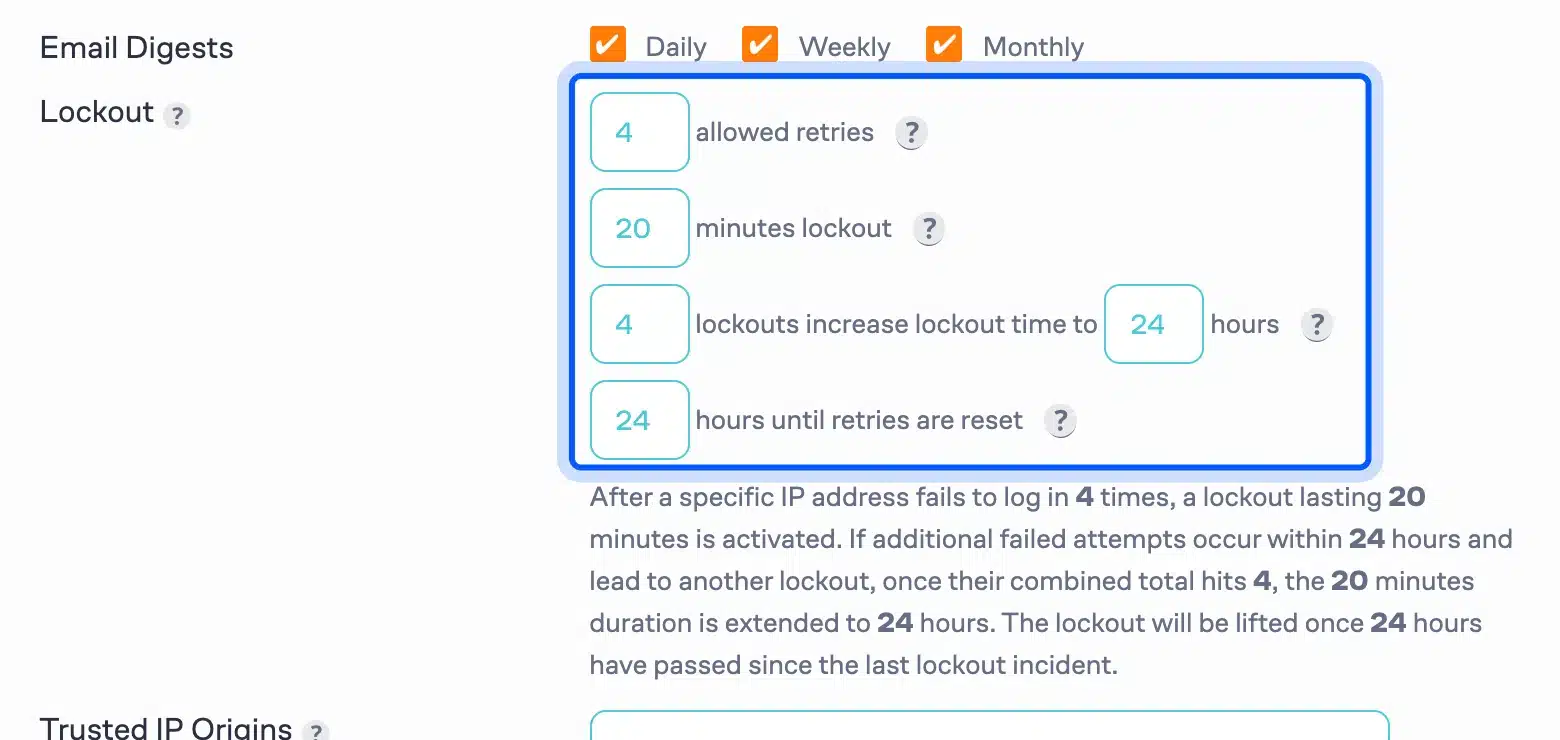
- Check the lockout limits: Scroll to the Local App section and find the Lockout row. The defaults are 4 allowed retries, a 20 minute lockout, and 24 hours after 4 lockouts. Change a value if you want a stricter limit. Then click Save Settings.
- Test the lockout: Open the login page in a private window and enter a wrong password until the plugin blocks you. On our site, the fourth failed attempt printed the lockout message.
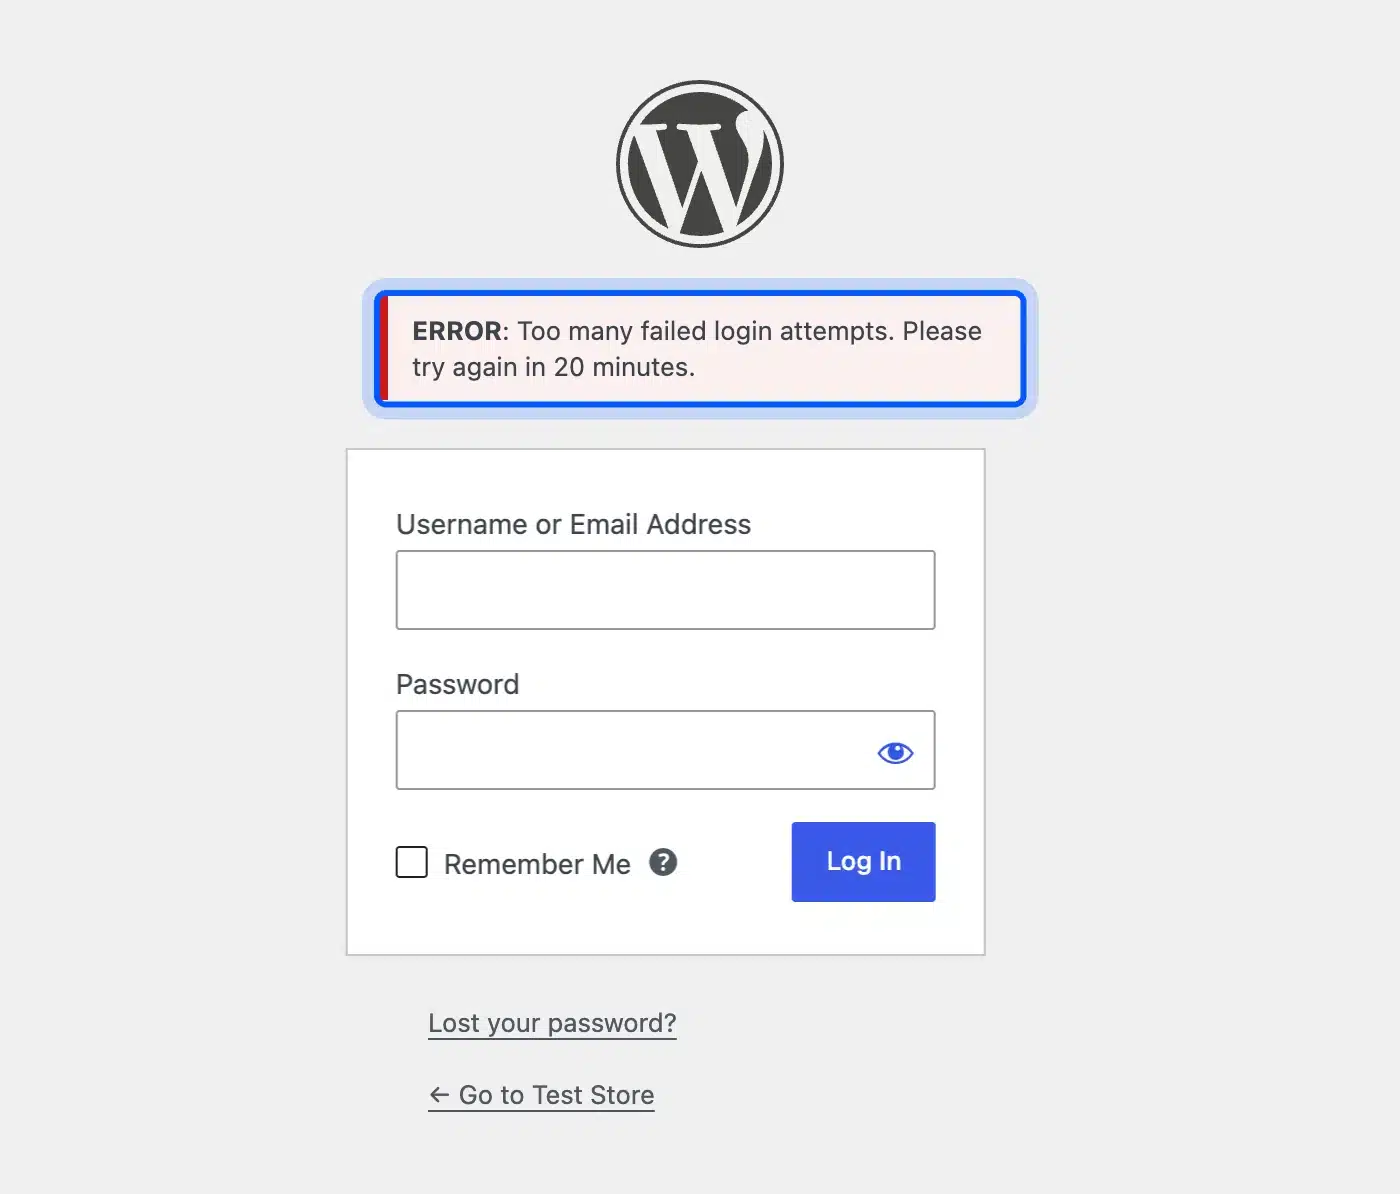
The first three failures showed a generic “Incorrect username or password” error. That is better than the core message, because it no longer confirms that a username exists.
Note: The settings screen also promotes a premium cloud app and a Micro Cloud option. You do not need either one for the local limits above. Trusted IP Origins is set to REMOTE_ADDR by default, and the plugin warns against changing it because other headers are easy to fake.
A limiter counts failed logins after they happen. A CAPTCHA stops scripts before they get that far, and a later section shows one in front of the login form.
Method 2: Limit Login Attempts in WordPress Without a Plugin
You can limit login attempts without a plugin by counting failures in a short PHP file. The code stores one counter per IP address and refuses logins once the counter reaches five. It uses only core WordPress functions and adds nothing to your plugin list.
Put the code in a must-use plugin instead of your theme’s functions.php file. WordPress loads files from wp-content/mu-plugins on every request, and a theme switch cannot remove them. The mu-plugins documentation says you cannot turn one off from wp-admin.
- Create the file: In
wp-content, add a folder namedmu-pluginsif it does not exist. Create a file namedlimit-login-attempts.phpinside it. - Paste the code: Copy the full snippet below into the file and save it.
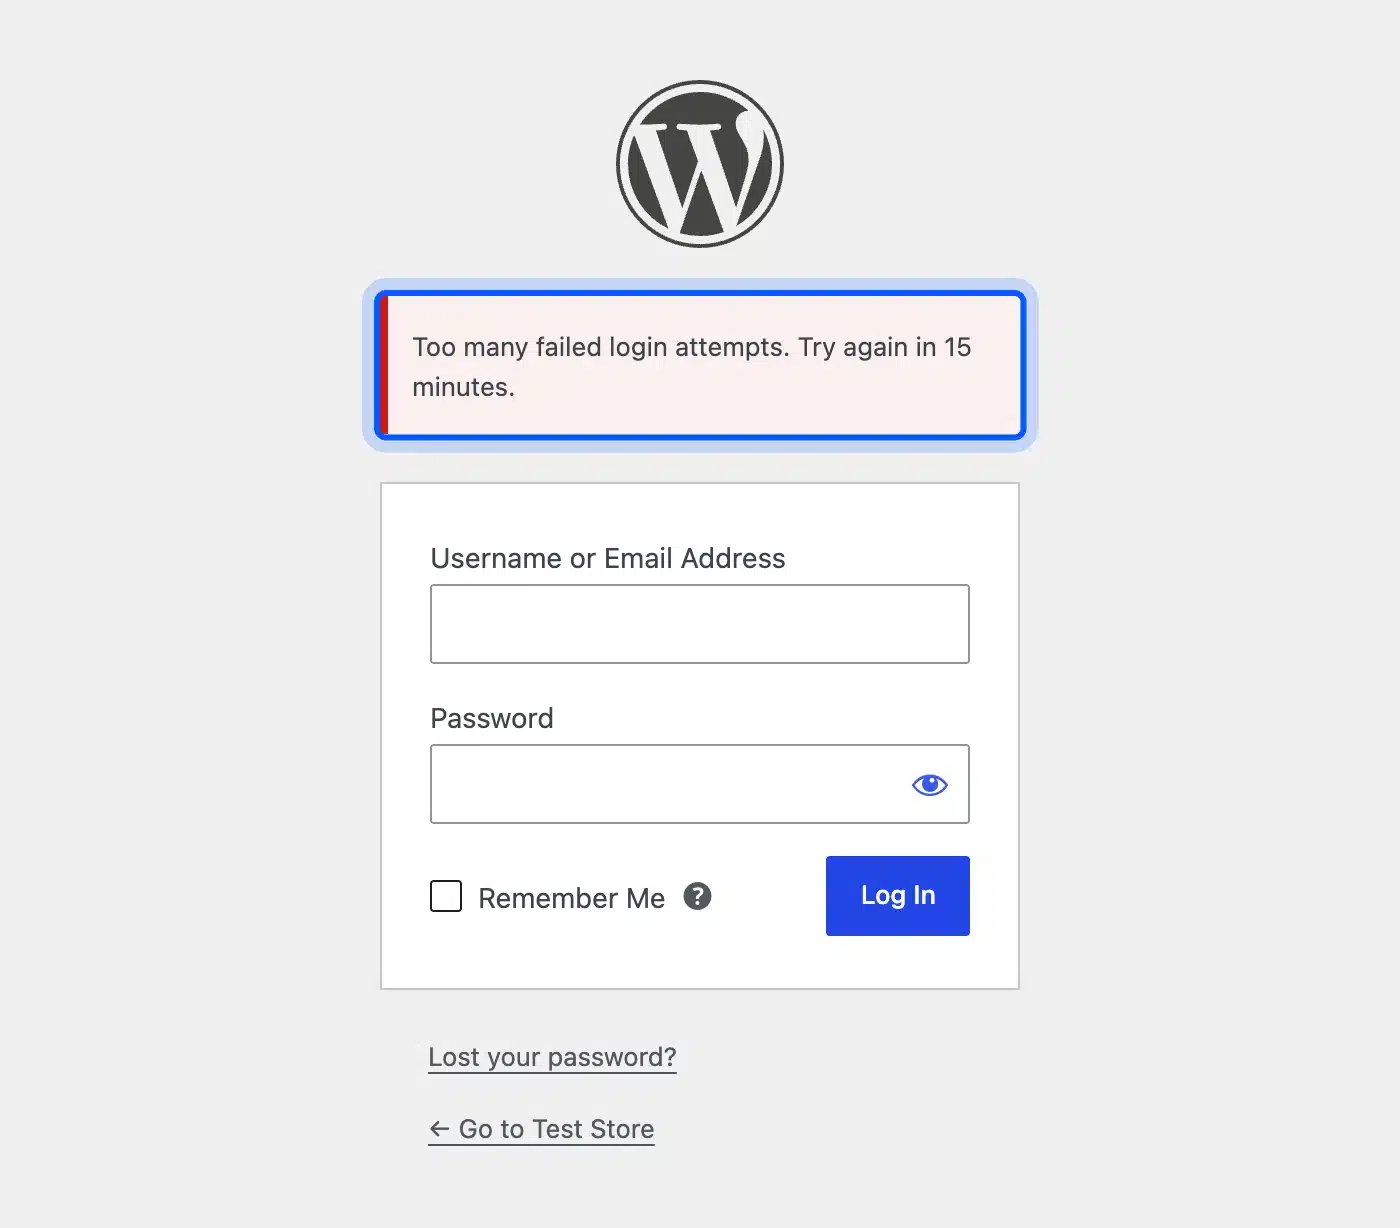
- Test it: Enter five wrong passwords in a private window. Then try a sixth. The sixth attempt should print the lockout message.
Here is the complete file:
<?php
/**
 * Plugin Name: Simple Login Limiter
 * Description: Locks an IP address out of every WordPress login after 5 failed attempts in 15 minutes.
 */

if ( ! defined( 'ABSPATH' ) ) {
	exit;
}

const DD_LOGIN_MAX_TRIES = 5;
const DD_LOGIN_LOCKOUT   = 15 * MINUTE_IN_SECONDS;

function dd_login_key() {
	return 'dd_login_' . md5( $_SERVER['REMOTE_ADDR'] ?? '' );
}

// Runs after WordPress has checked the password. A locked IP fails even with the right one.
add_filter(
	'authenticate',
	function ( $user ) {
		if ( (int) get_transient( dd_login_key() ) >= DD_LOGIN_MAX_TRIES ) {
			return new WP_Error(
				'too_many_attempts',
				sprintf( 'Too many failed login attempts. Try again in %d minutes.', DD_LOGIN_LOCKOUT / MINUTE_IN_SECONDS )
			);
		}
		return $user;
	},
	100
);

// Count each failure. Stop counting once locked. The lockout then does not keep extending.
add_action(
	'wp_login_failed',
	function () {
		$tries = (int) get_transient( dd_login_key() );
		if ( $tries < DD_LOGIN_MAX_TRIES ) {
			set_transient( dd_login_key(), $tries + 1, DD_LOGIN_LOCKOUT );
		}
	}
);

// A good login clears the counter.
add_action(
	'wp_login',
	function () {
		delete_transient( dd_login_key() );
	}
);
The filter runs late on purpose. The authenticate hook reference shows core checking passwords at priority 20 and a spam check at 99.
Priority 100 runs after both. An earlier priority could let a correct password slip through.
Our tests showed four behaviors worth knowing:
- Five tries: The first five wrong passwords printed the normal error, and the sixth printed the lockout message.
- Right password while locked: A correct password also failed until the lockout ended. That is intended, because a locked IP gets no further guesses.
- XML-RPC: Five wrong requests to
xmlrpc.phpalso filled the counter, and a correct password was then refused. The filter covers that endpoint too. - Reset: A successful login cleared the counter. Deleting the transient released a locked IP at once.
Warning: The code counts by REMOTE_ADDR. Behind Cloudflare or another proxy, that address can be the proxy’s and every visitor would share one counter.
We did not test behind a proxy. Check which IP your host reports before you use this on a live site.
This snippet has no email alert, no log and no allowlist. If you need those, use the plugin in Method 1.
Method 3: Limit Logins at Cloudflare or the Server
You can also limit login attempts before WordPress runs at all. A Cloudflare rule or a fail2ban jail blocks an IP at the edge or on the server without PHP answering the blocked request. That saves your server work during a flood.
The Cloudflare documentation names protecting a login endpoint from brute-force attacks as a use for these rules. The Free plan allows 1 rule, counts by IP, and uses a 10 second counting period and a 10 second mitigation timeout.
So a free rule can slow a fast script. It cannot build a 20 minute lockout like the plugin does.
On Nginx, the WordPress.org guide shows a limit_req_zone example. It allows 10 requests a minute with a burst of 20 on wp-login.php and xmlrpc.php. Our guide to protecting the WordPress admin URL in Nginx is a good next read if you run Nginx.
fail2ban works differently. It reads a log file and bans an IP at the firewall after repeated failures.
The WP fail2ban plugin writes WordPress login failures to the system log and ships fail2ban filters. It needs fail2ban running on a server you control. Confirm with your host that it is available.
We did not test Cloudflare or fail2ban. A real test needs a domain proxied through Cloudflare and a Linux server, and our test site runs on neither. If you run your own server, the fail2ban route is the strongest of the three.
Add a CAPTCHA in Front of Your Login Limiter
A CAPTCHA is not a limiter because it does not count failed logins. It asks a script to prove it is human before WordPress checks the password. Put it in front of a limiter and automated guessing meets two gates.
Our WooCommerce Advanced CAPTCHA plugin adds Cloudflare Turnstile, Google reCAPTCHA or hCaptcha to the WordPress login form. We tested the Pro build 1.1.0 on WordPress 7.1.3 with Cloudflare’s published test keys.
- Turn it on: Open DevDiggers Plugins > Advanced CAPTCHA > Configuration > General. Switch on Enable Advanced CAPTCHA and choose your provider. Paste its keys under Configuration > Cloudflare Turnstile.
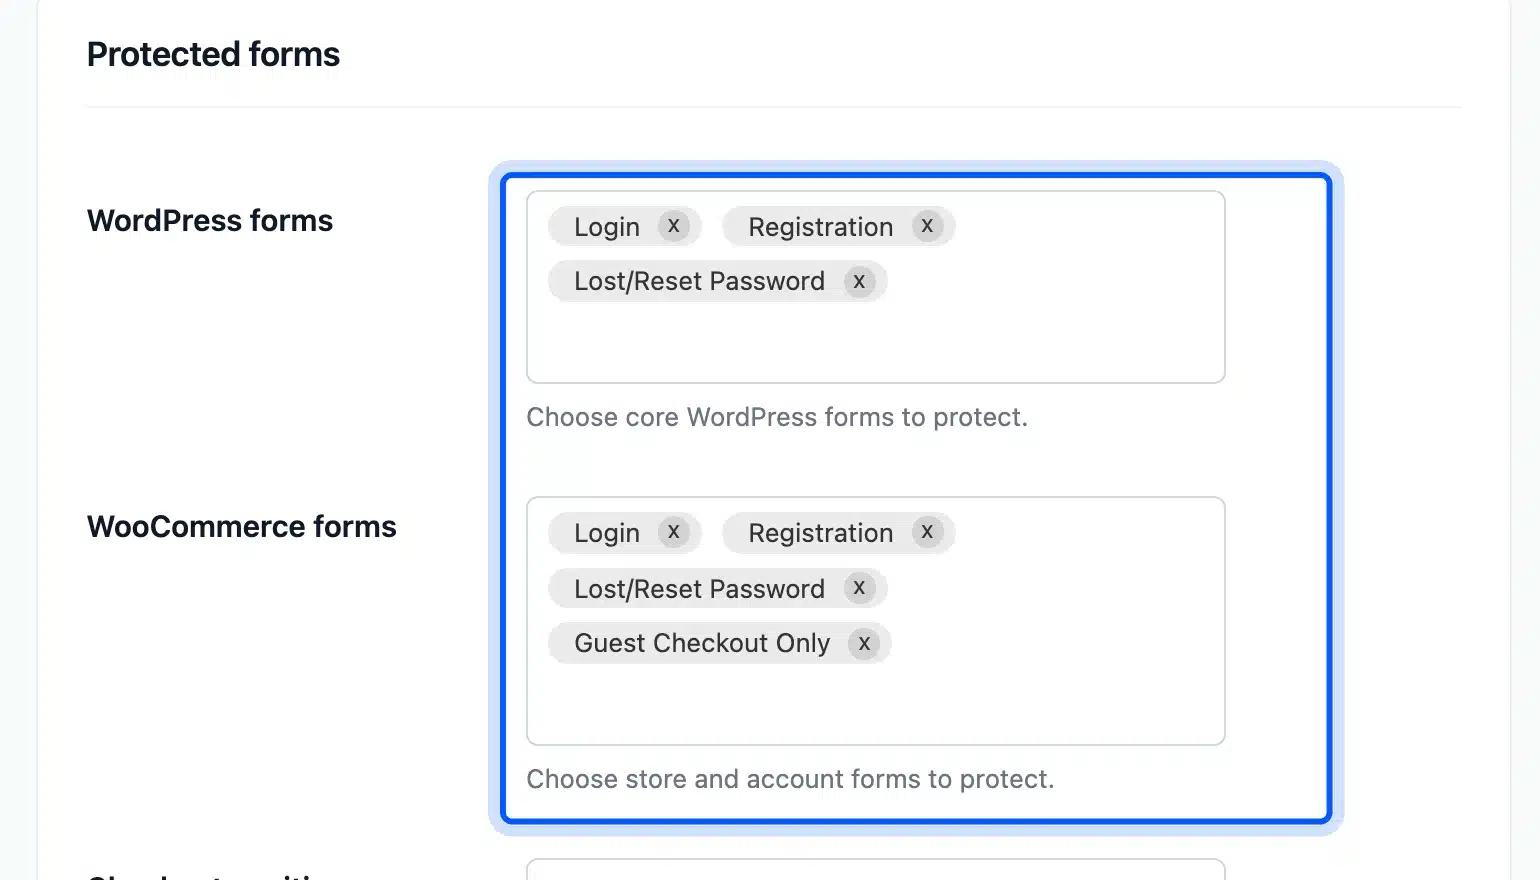
- Pick the form: Open Configuration > Forms. Under WordPress forms choose Login and click Save Changes.
- Check the login page: Open
/wp-login.phpin a private window. The widget sits above the Log In button and shows Success once it passes.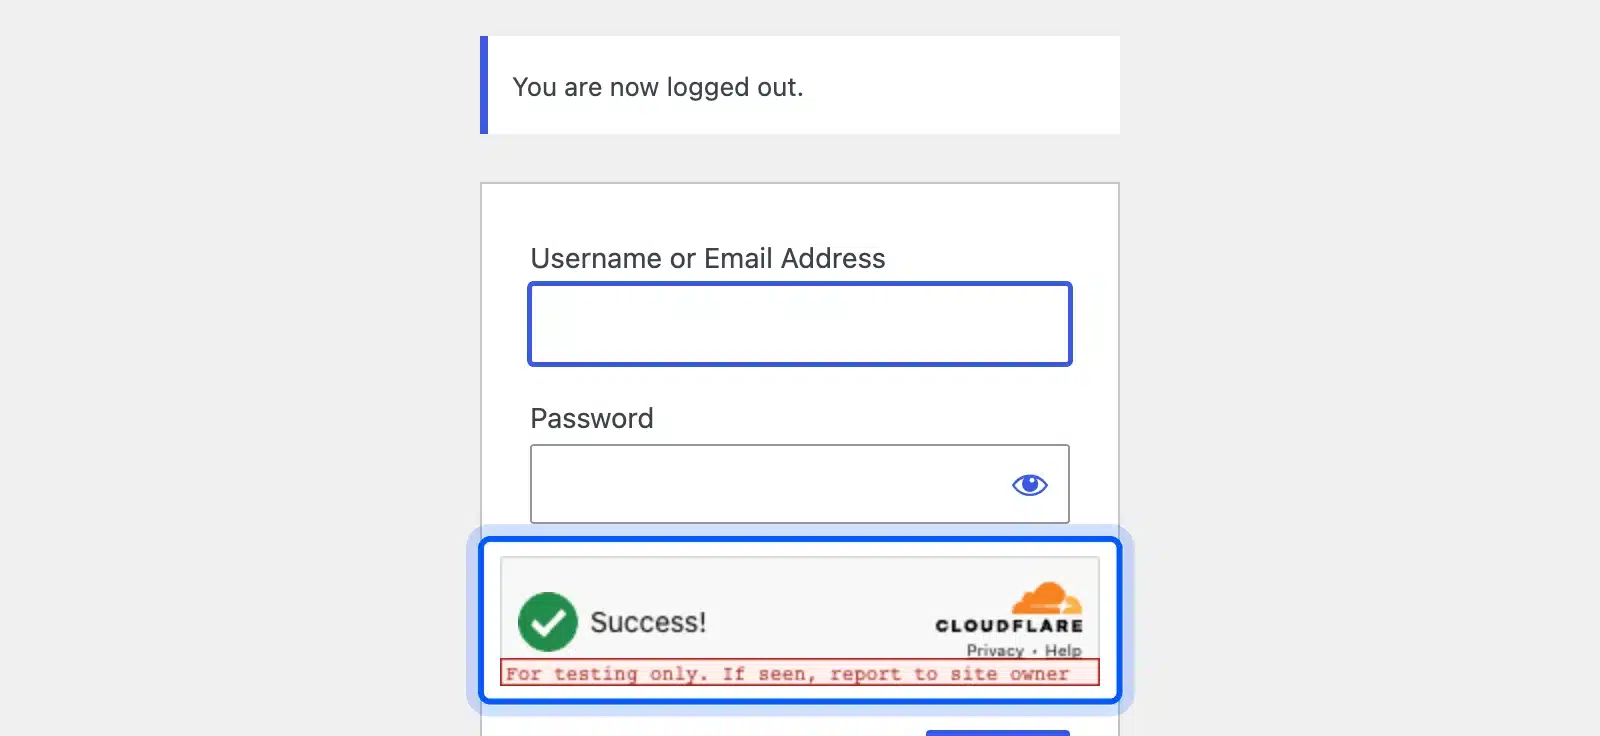
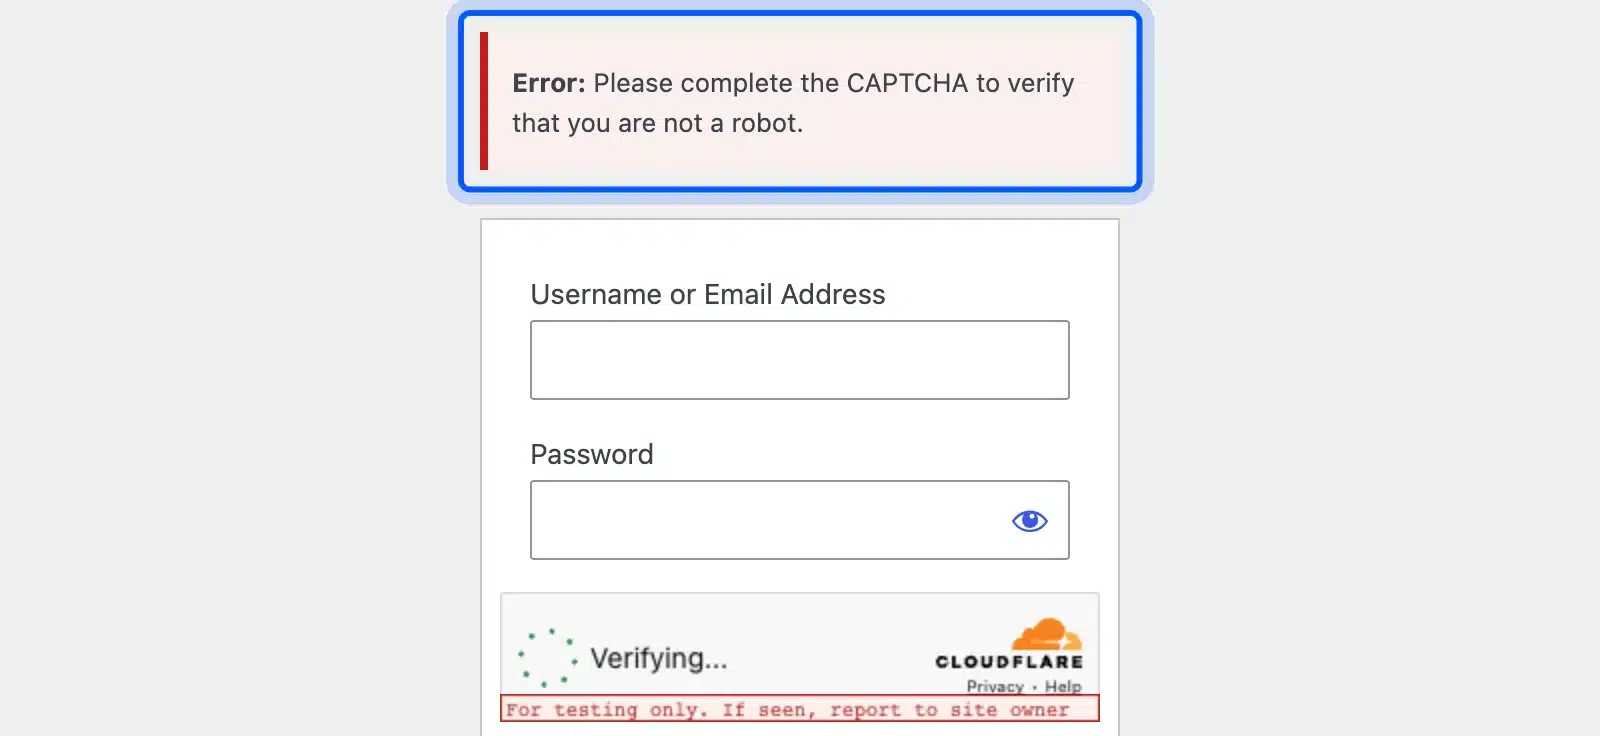
Here is what we saw. A login request with no CAPTCHA token was refused with “Please complete the CAPTCHA to verify that you are not a robot.” A solved widget let the login through.
The CAPTCHA also closed the xmlrpc.php login on our test site. With login CAPTCHA on, an XML-RPC login with the right password returned a 403 error. With it off, the same call worked.
Apps that sign in through XML-RPC stop working when you turn it on.
Warning: Save the secret key before you log out. With the secret empty, every protected form refused logins on our test site, and that includes the administrator login.
Our WordPress security checklist walks through every step with screenshots.
What .htaccess Can and Cannot Do for Login Security
An .htaccess file can allow or deny IP addresses and ask for a password, but it has no counter for failed logins. The WordPress.org guide says Apache request throttling needs extra tools such as ModSecurity or mod_evasive. A plain rule that claims to lock out after three failures is not counting anything.
We tested the popular “counter” rule that uses SetEnvIf and a RewriteCond on %{ENV:LIMIT_LOGIN_ATTEMPTS}. On our Apache 2.4 test site, it returned 403 Forbidden for wp-login.php on the very first visit.
The variable holds the visitor’s IP address and never a count. The rule never counted anything.
Two things in .htaccess do work, and we tested both:
- IP allowlist: A
Require iprule inside a<Files wp-login.php>block returned 403 to our address when it was not listed, and 200 when it was. This suits an admin who always logs in from one fixed IP. - Basic authentication: A password prompt on
wp-login.phpreturned 401 to no credentials and to six wrong ones, and 200 to the right one. It adds a second gate but never locks anyone out.
Both rules help, and neither one limits attempts. Keep a backup of the file before you edit it, because a typo in .htaccess can take the whole site offline.
The same guide shows the allowlist form in its Apache examples, and it asks you to test in staging before production. That advice fits here, since a wrong Require ip line locks you out of your own login page.
How to Test Your Lockout and Get Back In
Test every limiter from a private browser window before you trust it. Enter wrong passwords until the lockout message appears and confirm that a correct login works after the lockout time. If you lock yourself out, wait it out or remove the limiter through your files.
Use this order if you are locked out of a live site:
- Plugin lockout: Wait for the lockout time, or rename the plugin folder
limit-login-attempts-reloadedinwp-content/pluginsover FTP or your host’s file manager. WordPress then deactivates it. - Snippet lockout: Delete the file from
wp-content/mu-plugins, or wait 15 minutes. With WP-CLI, runwp transient delete --allto clear every stored counter. - Wrong IP trusted: If a proxy makes everyone share one address, fix the IP source first. Then clear the counters.
Add your own IP to the plugin’s allowlist after you confirm the lockout works. That keeps a typo from costing you twenty minutes.
Test with a throwaway account when you can. Locking out the username you use every day means a wait, while a spare user costs nothing. Also confirm that the lockout message appears on the login screen, since a blank error tells you nothing.
After the limiter is live, check it once a month. Open a private window, trigger the lockout, and confirm the message still shows. A plugin update or a new caching rule can change how the login page behaves.
Conclusion
To limit login attempts in WordPress, start with Limit Login Attempts Reloaded. Its defaults of 4 tries and a 20 minute lockout worked on our test site without any changes. Use the PHP snippet when you want no extra plugin, and add a Cloudflare or fail2ban rule when login traffic strains your server.
Skip any .htaccess rule that claims to count failures, because it cannot. For deeper protection, read our WordPress brute force protection guide and the full WordPress security checklist. If you would rather hand this work over, our WordPress security services cover it.
Frequently Asked Questions (FAQs)
Q1. How many failed login attempts should WordPress allow?
Three to five is a sensible range for a login limiter. Limit Login Attempts Reloaded defaults to 4 allowed retries before a 20 minute lockout. Our snippet allows 5, and you can change one constant to tighten it.
Q2. How do you reset too many failed login attempts in WordPress?
Wait 20 minutes for the lockout to end in Limit Login Attempts Reloaded. If you cannot wait, rename the plugin folder over FTP to deactivate it. For the code snippet, delete the file or run wp transient delete --all.
Q3. Does limiting login attempts also protect XML-RPC?
It can, if the limiter hooks the authenticate filter that XML-RPC logins also pass through. We tested our snippet against xmlrpc.php, and five wrong requests filled the counter. Check your plugin’s documentation before you rely on it for that endpoint.
Q4. Does a login limiter replace two-factor authentication?
No, the two do different jobs. A limiter slows guessing, while two-factor authentication adds a second proof after the password. The WordPress.org brute force guide notes that core has no two-factor authentication and you need a maintained plugin.
Q5. Why does WordPress tell me which username is wrong?
On our test site, the default login error named the username and called its password incorrect. That confirms the account exists. Limit Login Attempts Reloaded printed a generic error instead and no longer confirms which usernames are real.
Q6. Should I use a plugin or Cloudflare to limit logins?
Use the plugin first, because it gives you logs, alerts and an allowlist with no server access. Add a Cloudflare rule when attackers strain your server. The two work well together, since the rule blocks floods and the plugin handles slower guessing.




