WordPress DDoS protection is the combination of tools, server configurations, and network-level defenses that stop attackers from flooding your site with fake traffic until it crashes.
Cloudflare mitigated 23.2 million network-layer DDoS attacks in the first half of 2026, according to its DDoS Threat Report for H1 2026. Most WordPress sites still run on a basic setup with one or two tools. We checked every plan detail and statistic in this guide against Cloudflare, Patchstack and WordPress documentation in October 2026.
This article covers what makes WordPress sites vulnerable and how attacks hit specific WordPress files and endpoints. It then shows how to build a layered defense and what to do if an attack is already underway.
What a WordPress DDoS Attack Looks Like
A DDoS (Distributed Denial of Service) attack floods your server with requests from thousands of devices at once. The goal is to exhaust your server’s resources: CPU, memory, or bandwidth, until legitimate users can no longer reach your site. The devices doing the flooding are usually part of a botnet: a network of compromised machines controlled by an attacker without their owners knowing.
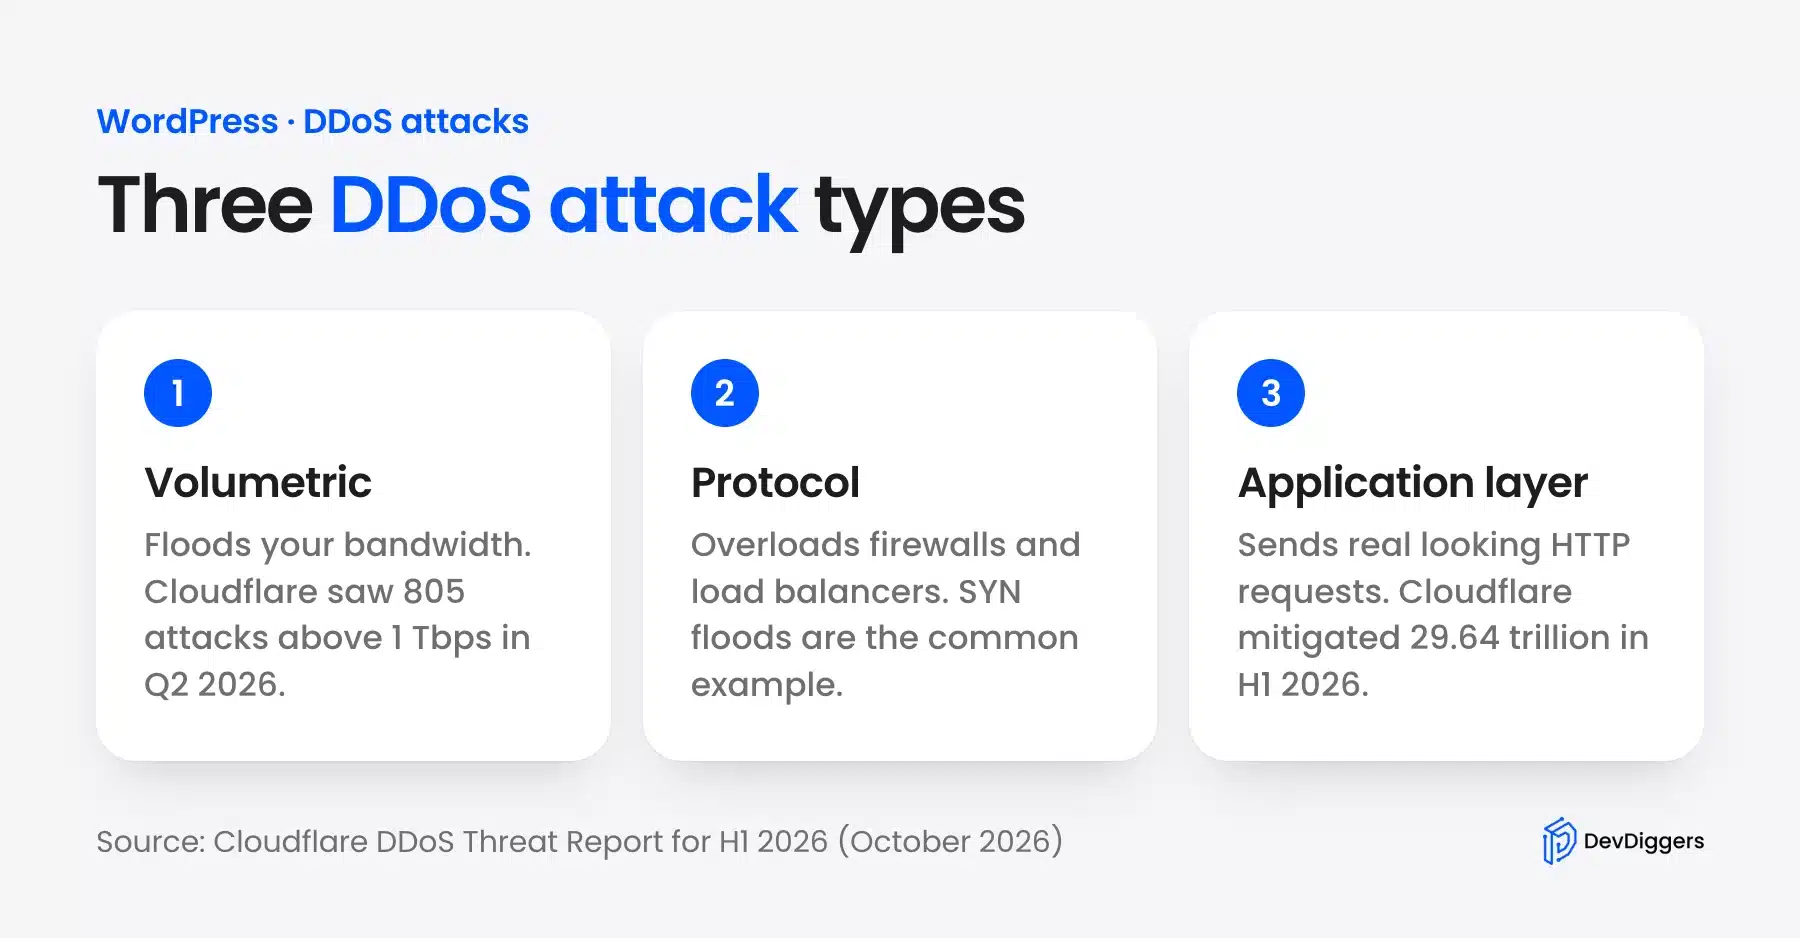
There are three distinct types to understand, because the protection that works against one does not always work against another.
- Volumetric attacks try to saturate your bandwidth. The sheer volume of data overwhelms your network before any request even reaches WordPress. Cloudflare counted 805 attacks above 1 Tbps in Q2 2026, up 519% from Q1, in its DDoS Threat Report for H1 2026.
- Protocol attacks target your server’s network stack, overloading firewalls and load balancers rather than WordPress itself. SYN floods are the most common example.
- Application-layer attacks are the most relevant for WordPress. Instead of flooding bandwidth, they send HTTP requests that look like real traffic. Each request forces your server through the full WordPress execution stack: loading PHP, initializing all active plugins, running database queries, and rendering output. A WordPress site with 20 to 30 active plugins has a high cost per request. Under normal traffic, caching handles this well. Under an attack sending thousands of concurrent requests, the server runs out of PHP workers fast.
Cloudflare mitigated 29.64 trillion HTTP DDoS requests in the first half of 2026, per its DDoS Threat Report for H1 2026. That is the attack type most likely to hit a WordPress or WooCommerce site.
How to Tell It’s a DDoS Attack (Not Just a Traffic Spike)
A sudden traffic surge could be a viral post or a DDoS attack. Here is how to tell the difference.
With a genuine traffic spike, requests come from many different locations but follow normal browsing patterns: people land on your homepage or a specific post, stay for a while, and click around. Server load rises, but your error logs stay mostly clean.
With a DDoS attack, you will see requests hitting the same endpoint repeatedly from hundreds or thousands of IP addresses. Your server logs fill up with POST requests to /xmlrpc.php or GET requests to /wp-login.php at a rate no human browsing session could produce. CPU and memory spike hard and fast. Your hosting provider may alert you to unusual resource use before you even notice the slowdown. To see which addresses are behind the traffic, read how to find the IP address of a WordPress site, including the address a proxy hides.
Check your access logs first. On Apache, run grep xmlrpc.php /var/log/apache2/access.log | wc -l and check the count. A high number of POST requests from different IPs in a short window is a strong indicator. On Nginx, check /var/log/nginx/access.log.
If your login page shows large numbers of rapid, varied login attempts from many IPs, that is more likely a brute-force attack than a DDoS. The two often run together, but they need different responses.
The WordPress Attack Vectors Attackers Use
Most guides treat xmlrpc.php, wp-login.php, and the REST API as separate issues. Attackers do not. They probe all three and hit whichever one is easiest. Here is what each one does in a DDoS context.
xmlrpc.php: Two Threats and Not One
The xmlrpc.php file is a legacy WordPress feature that allowed remote publishing from old desktop apps and early mobile clients. It has two specific DDoS uses that are often confused.
The first is pingback abuse. Attackers send spoofed pingback requests through your xmlrpc.php to flood a third-party target, without your knowledge. In one documented attack, security researchers at Sucuri found over 162,000 legitimate WordPress sites unknowingly hitting a single target through this method. Your site becomes part of the botnet. Your hosting provider may suspend you. You will not know it happened until you check your logs or get a notice.
The second is brute-force amplification. The system.multicall method lets an attacker bundle hundreds of password attempts into a single HTTP request. A plugin watching /wp-login.php for suspicious login activity will not see any of it. The requests never touch that file.
wp-login.php Flooding
This is the bluntest attack vector. Attackers send thousands of requests to the WordPress login page to exhaust server resources or eventually guess credentials.
Cloudflare’s own data shows how much of this traffic is automated. It found that 76% of leaked-password login attempts on WordPress sites succeed and 48% of those successful logins are bot-driven (Cloudflare, March 2025).
WordPress REST API Endpoint Abuse
Less discussed, but growing. The REST API is a modern interface that allows plugins, themes, and external tools to interact with WordPress using JSON. Attackers send unauthenticated requests to REST API endpoints at high volume.
Each request still runs PHP and hits the database. A flood of unauthenticated REST API calls costs your server the same as a flood of page loads that skip the cache.
Worth knowing: A common recommendation is to disable the REST API entirely for unauthenticated users. That creates a serious problem for WooCommerce, which we cover next.
WooCommerce Specific DDoS Risks
WooCommerce stores face more DDoS risk than a blog because their busiest pages cannot be cached. Cart, checkout and search run PHP and database queries on every request. The Store API that powers the cart and checkout blocks must also stay open to logged-out shoppers.
A standard WordPress blog has one main attack surface: the homepage, posts, and the login page. A WooCommerce store has several more.
Checkout and Cart Pages
Each checkout request involves session handling, inventory checks, payment gateway communication, and order creation. That per-request cost is significantly higher than a simple blog post. Attackers targeting application-layer vulnerabilities know this.
A few thousand concurrent checkout requests can bring a store to its knees faster than the same number of homepage requests.
Product Search on Large Catalogs
A search query on a catalog with thousands of products triggers a database-heavy operation. Automated requests hitting your search endpoint at volume will exhaust your database connections quickly.
This is a common pattern in attacks against WooCommerce stores.
The REST API Trade-Off
WooCommerce depends on the REST API. The product blocks in the block editor, cart synchronization, mini-cart updates, and order management all use it. If you disable the REST API for unauthenticated users, you will break your storefront.
Product blocks stop rendering. The minicart stops updating. Checkout fails for some users, depending on your theme and setup.
The correct approach is not to disable the REST API. It is to rate-limit it and restrict sensitive endpoints to authenticated users only. More on that in the next section.
Timing Matters
Plan for an attack during your busiest periods: sales events, product launches and holiday campaigns. Downtime costs the most then, and a motivated attacker knows when your site needs to be online.
Patchstack’s State of WordPress Security in 2026 found that the weighted median time to first exploit of a heavily targeted flaw was 5 hours. For WooCommerce stores that window is tight, especially during a high-traffic period with no monitoring in place.
For a broader view of hardening your WooCommerce store beyond DDoS, our WooCommerce security checklist covers the full security picture.
DDoS Protection Plugins vs Hosting vs a CDN
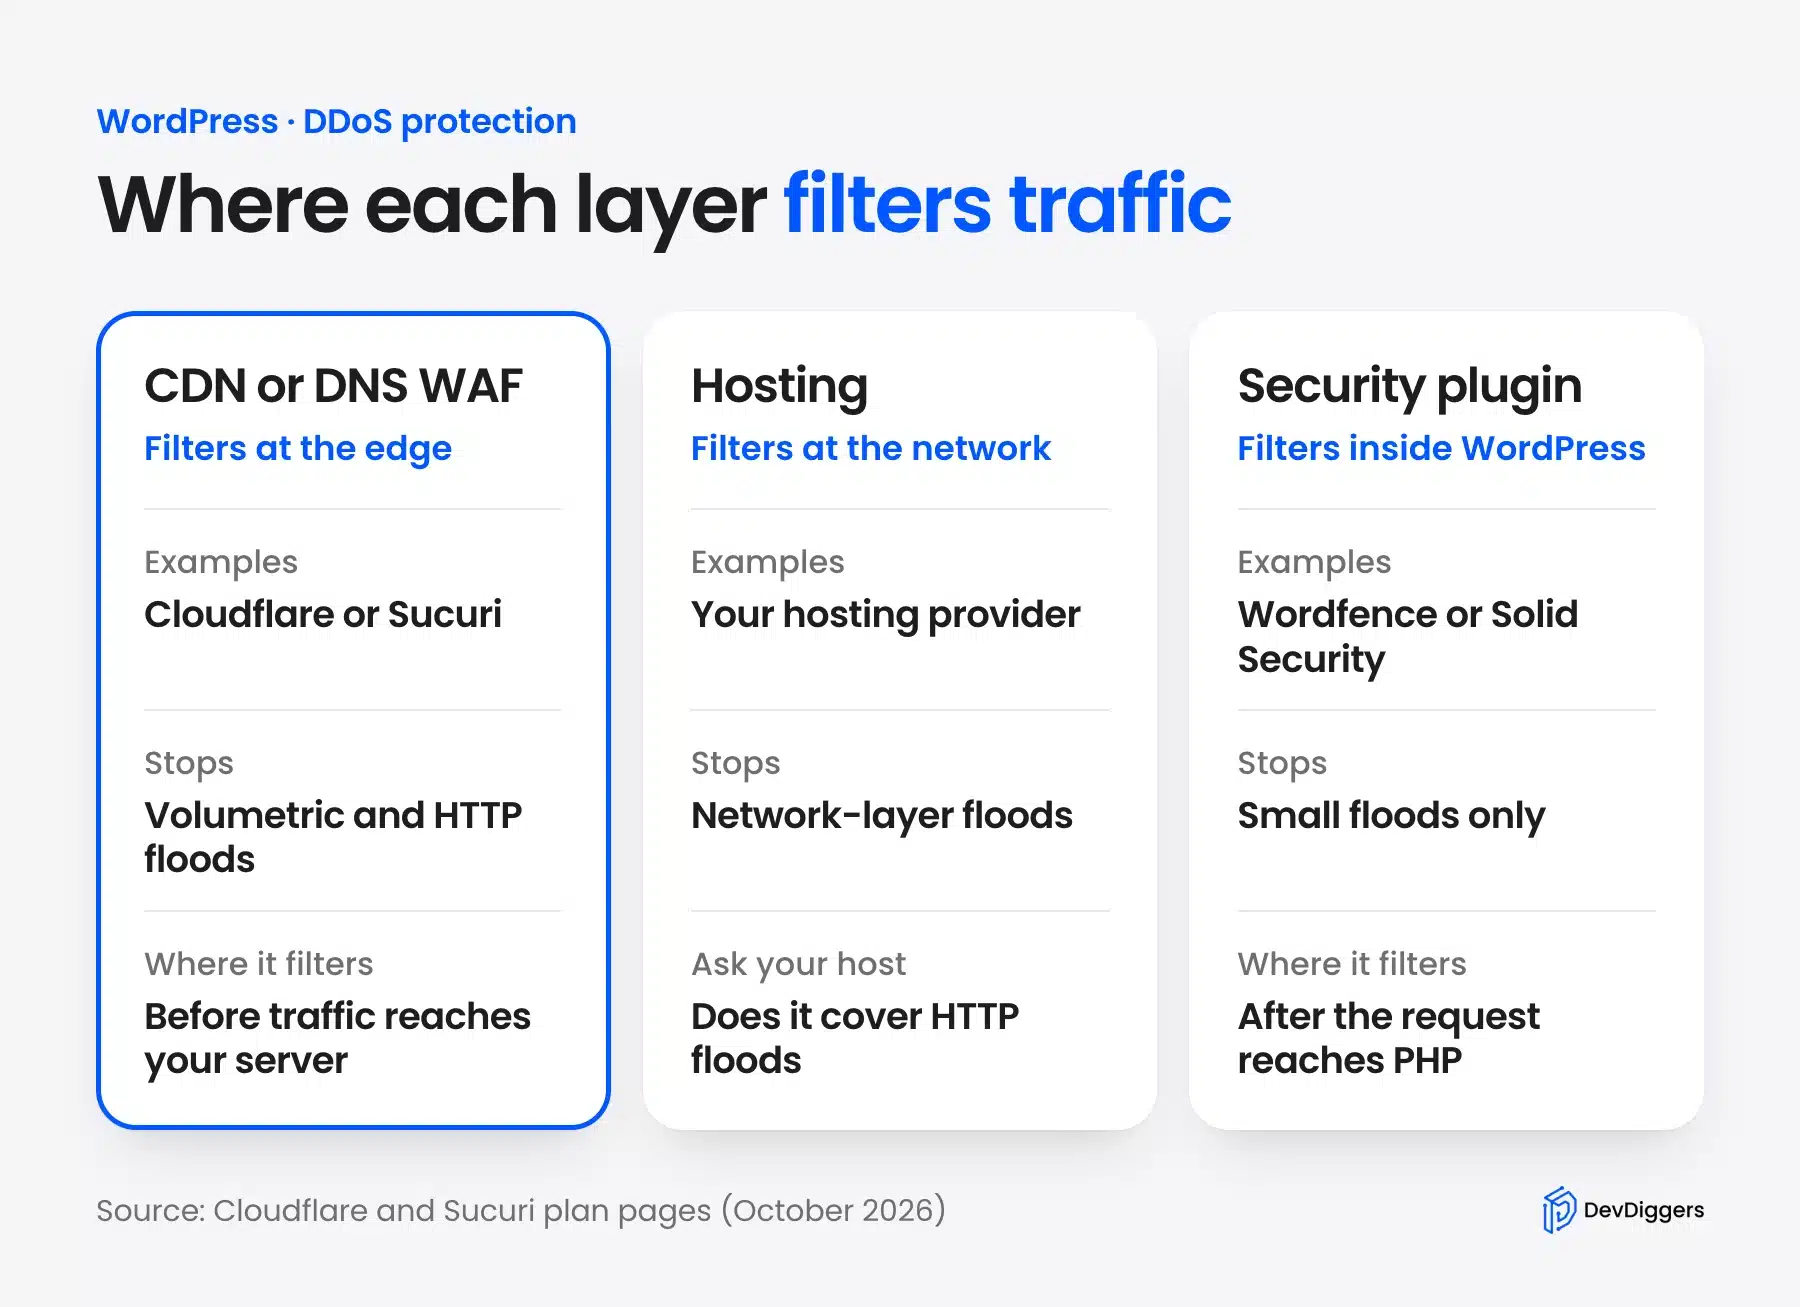
DDoS protection works by filtering bad traffic before it uses up your server. Where that filter sits decides what it can stop. A CDN or DNS-level WAF filters at the edge, hosting protection filters at the network and a plugin filters only after the request reaches WordPress.
There are three places you can add protection. Each one stops a different kind of flood.
- CDN or DNS-level WAF: Cloudflare or Sucuri filters traffic at the edge before it reaches your server. It stops volumetric floods and HTTP floods, and Cloudflare’s version is free.
- Hosting with DDoS protection: The host filters floods at its network edge. Ask your host whether that covers HTTP floods or only network-layer attacks.
- Security plugin: Wordfence or Solid Security filters requests inside WordPress. By then each request has already reached PHP. It helps only against small floods.
A plugin cannot stop a flood that has already filled your bandwidth. Use it for login protection and malware scans, and put a CDN or WAF in front of the site for DDoS.
How to Layer Your WordPress DDoS Protection
No single tool stops all attack types. A plugin alone will not stop a volumetric attack. A CDN alone will not block application-layer attacks targeting your authenticated endpoints. You need layers.
Layer 1: DNS-Level WAF and CDN
This is the most important layer, and its basic version costs nothing on Cloudflare’s free plan.
A web application firewall at the DNS level sits in front of your server. Traffic from visitors hits Cloudflare or Sucuri first, before it ever reaches your origin server. Volumetric attacks are absorbed at the edge network. Application-layer traffic is filtered before PHP runs.
This is fundamentally different from a plugin-based WAF. A security plugin like Wordfence is an application-level WAF. It blocks traffic after it hits your server. During a volumetric attack, your server is already overwhelmed before Wordfence sees the request. Application-level WAFs are useful for many threats. They are not the right tool for DDoS mitigation on their own.
- Cloudflare: Every Cloudflare plan gets unmetered DDoS protection for layers 3 to 7, the Free plan too. It includes one rate limiting rule and the Free Managed Ruleset. Pro and higher add the full Cloudflare Managed Ruleset and the OWASP Core Ruleset (as of October 2026).
- Sucuri: The Basic Firewall starts at $9.99 a month (as of October 2026). It runs at the DNS level and covers network and HTTP attacks.
During an active volumetric attack, Cloudflare’s “I’m Under Attack” mode adds a JavaScript challenge that blocks most bots while letting real browsers through.
Layer 2: WordPress-Specific Hardening
Once edge protection is in place, tighten the WordPress-specific attack vectors. Here are the steps in order of impact.
1. Block or Restrict xmlrpc.php at the Server Level
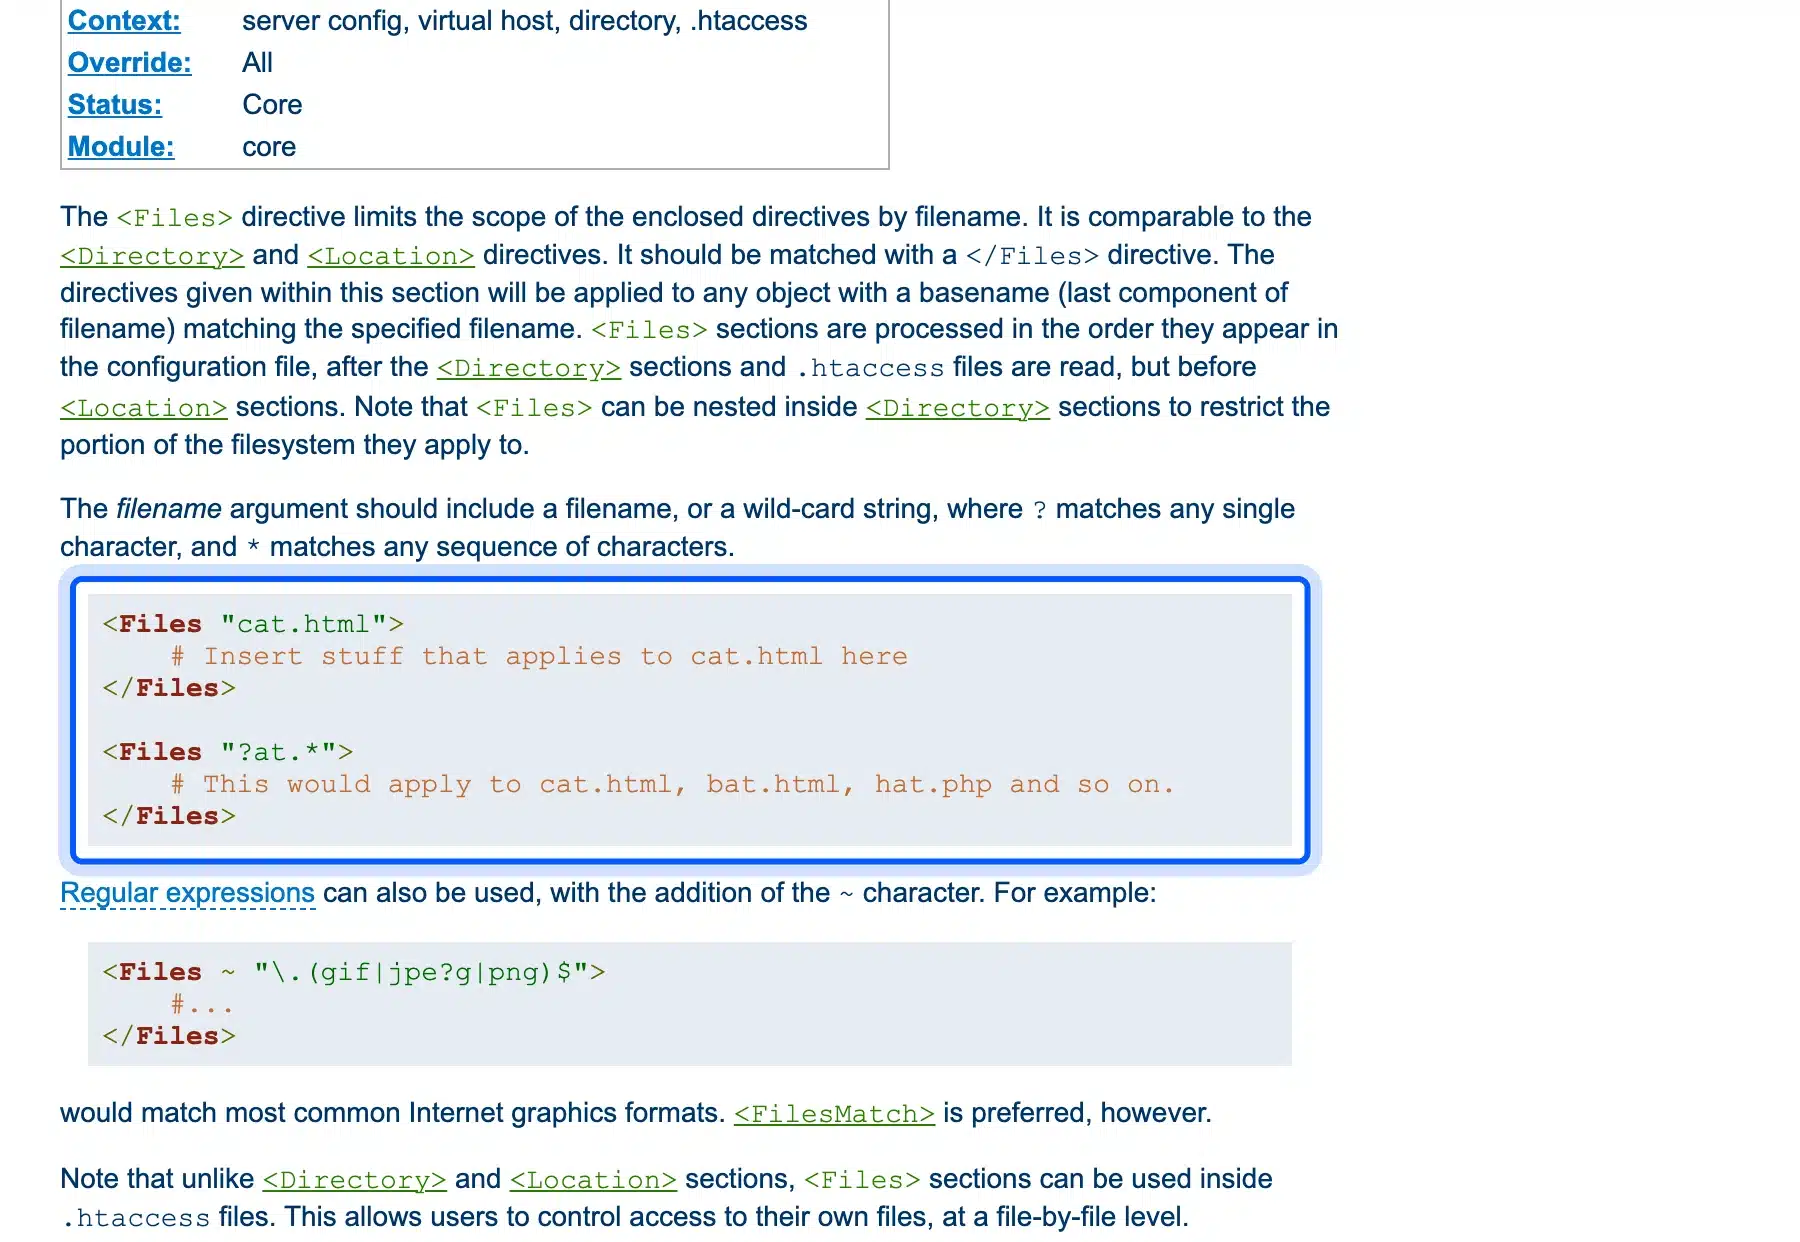
Do not rely on the xmlrpc_enabled filter in PHP. The WordPress developer reference says it only turns off methods that need a login. Pingbacks still work. Block the file at the server level instead.
On Apache 2.4, add this to .htaccess:
# Block WordPress xmlrpc.php requests
<Files xmlrpc.php>
  Require all denied
</Files>
On Nginx:
location = /xmlrpc.php {
  deny all;
}
Do not delete the file itself. WordPress core updates will restore it. Block access instead.
Warning: If you use Jetpack, it relies on xmlrpc.php for its connection to WordPress.com. Keep xmlrpc.php open to Jetpack by allowing its published IP ranges. Block everyone else.
2. Rate limit wp-login.php
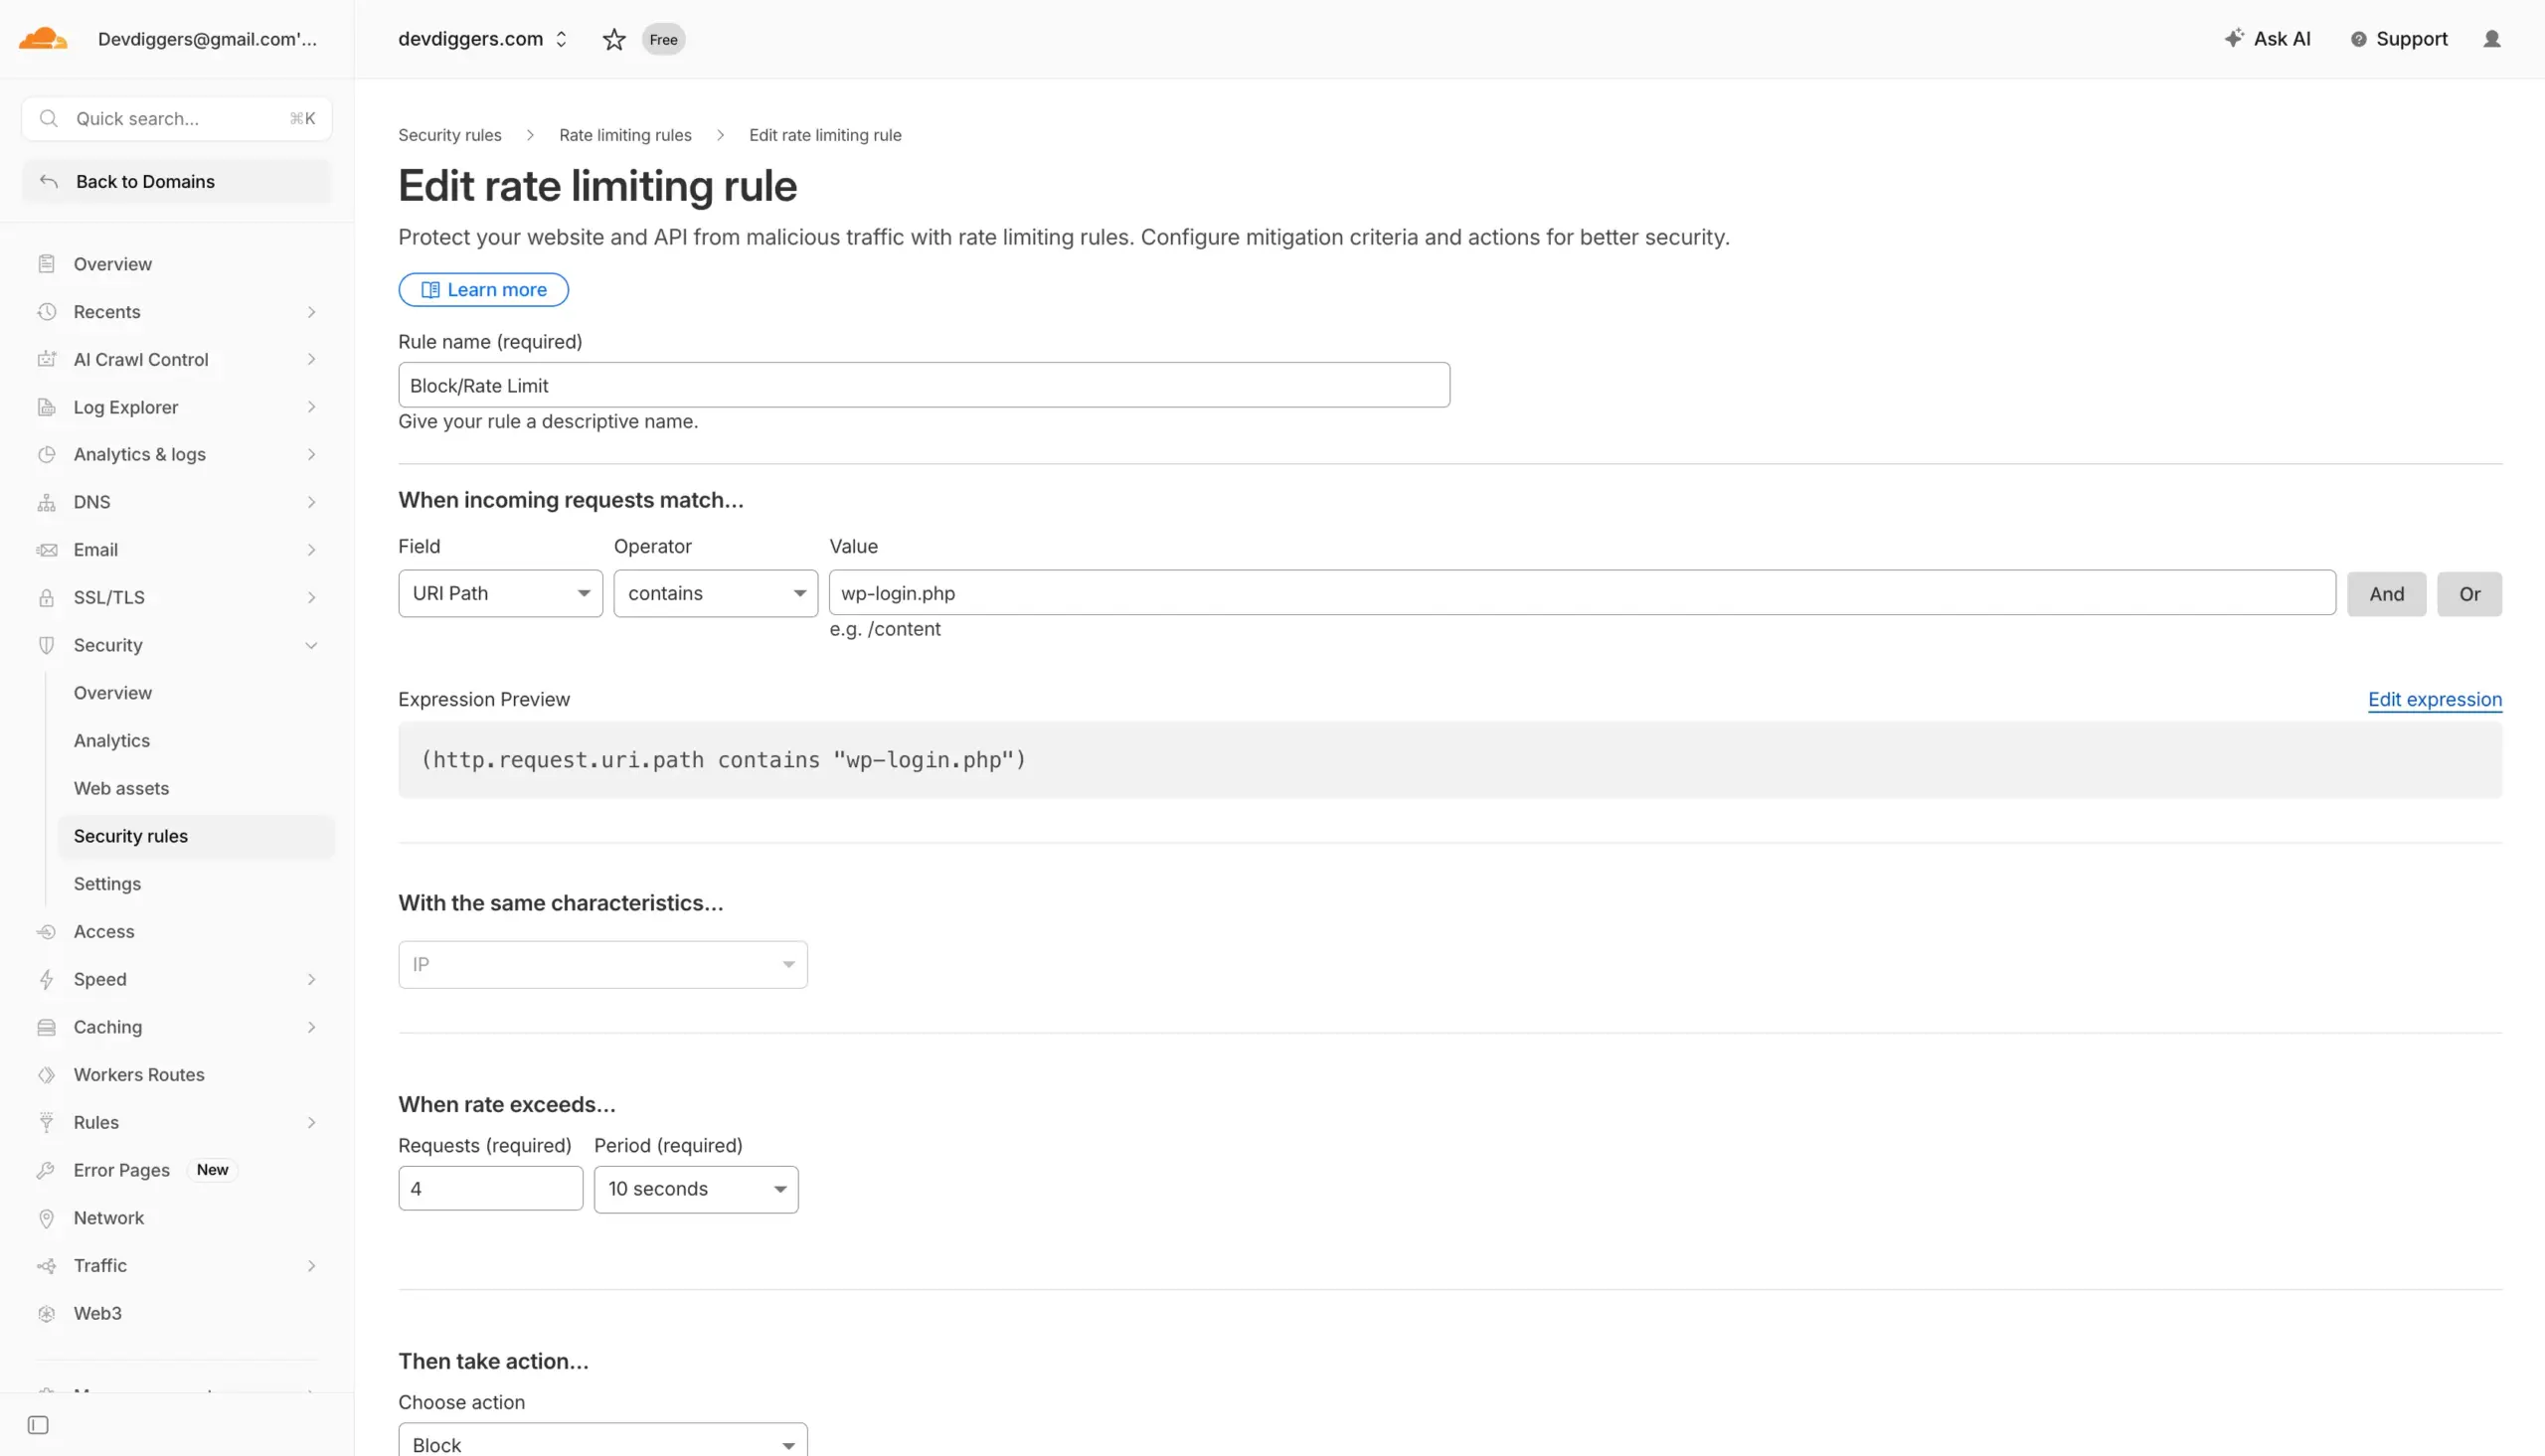
Your WAF or CDN should handle this. In Cloudflare, create a rate limiting rule for the path /wp-login.php. The free plan counts requests per IP over 10 seconds, and about 5 requests in that window is a fair starting point.
Without a CDN, ask your host about mod_evasive or a similar module. It runs at the Apache server level and cannot be set up in .htaccess.
3. Rate-Limit and Selectively Restrict REST API Endpoints
To protect WooCommerce without breaking it, let logged-out visitors reach only the routes your storefront needs. The cart and checkout blocks use the Store API under /wc/store/. Add this to a code snippet plugin or your child theme’s functions.php:
add_filter( 'rest_pre_dispatch', function( $result, $server, $request ) {
  if ( is_user_logged_in() ) {
    return $result;
  }
  // Public routes logged-out visitors still need.
  $allowed = array( '/wc/store/', '/oembed/' );
  $route   = $request->get_route();
  foreach ( $allowed as $prefix ) {
    if ( 0 === strpos( $route, $prefix ) ) {
      return $result;
    }
  }
  return new WP_Error( 'rest_restricted', 'REST API access restricted.', array( 'status' => 401 ) );
}, 10, 3 );
The route comes from the REST request object. That way the check also covers the ?rest_route= form of the URL. Add the namespace of any plugin that needs public REST access, like a form plugin. Pair this with a WAF rate limit on /wp-json/.
4. Disable Pingbacks and Trackbacks
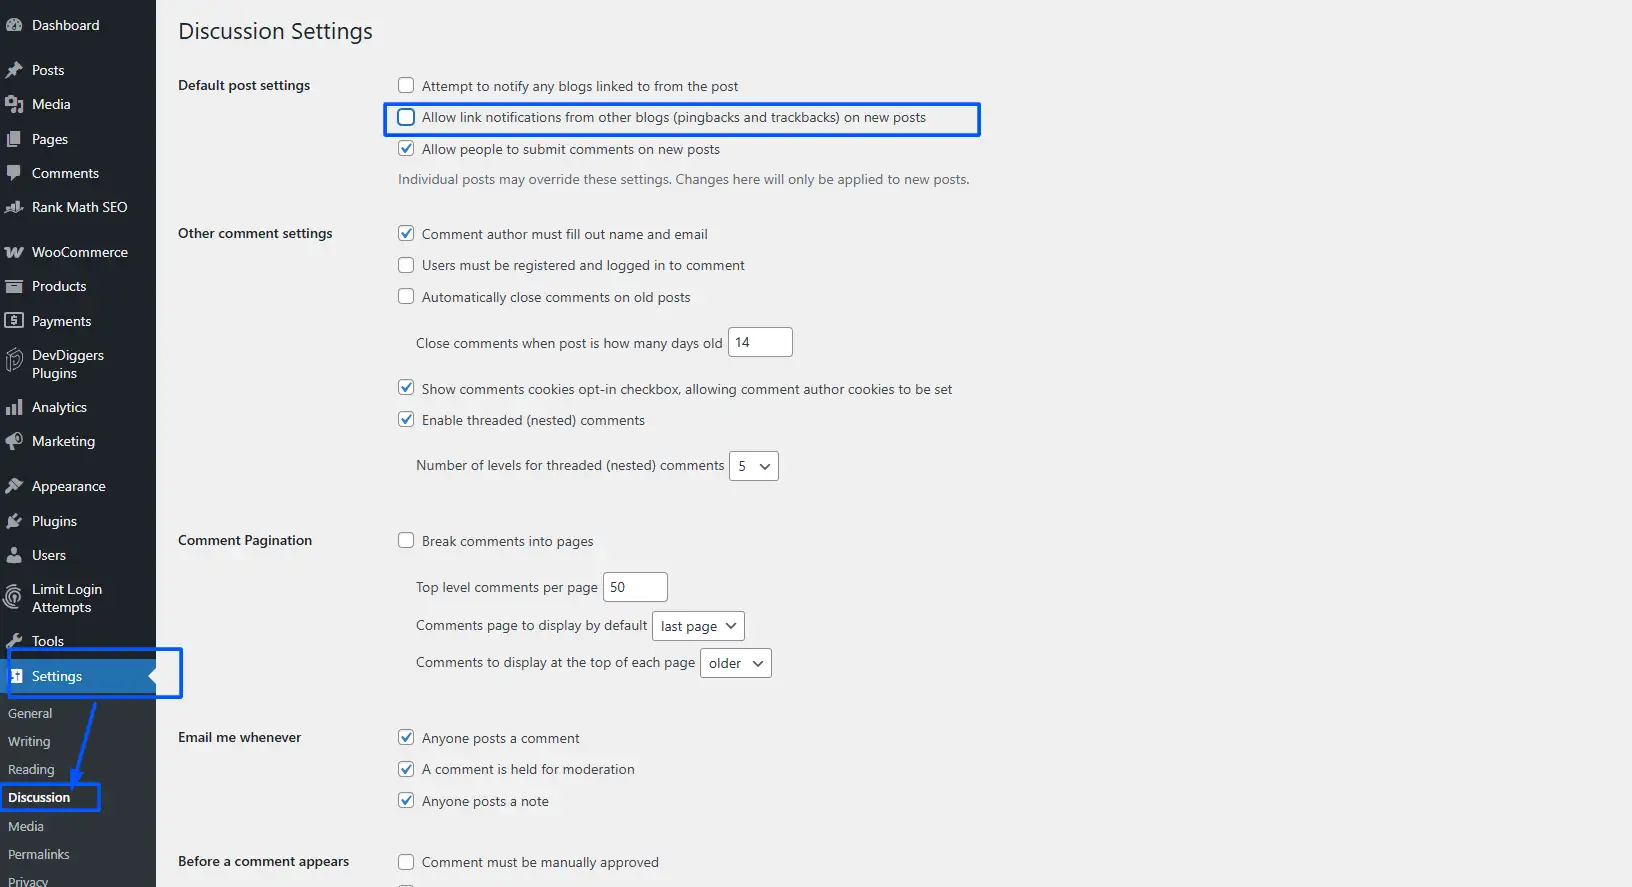
Go to Settings > Discussion in your WordPress dashboard. Uncheck “Allow link notifications from other blogs (pingbacks and trackbacks) on new posts.” This removes one pingback abuse vector at the WordPress level.
5. Enable Page Caching
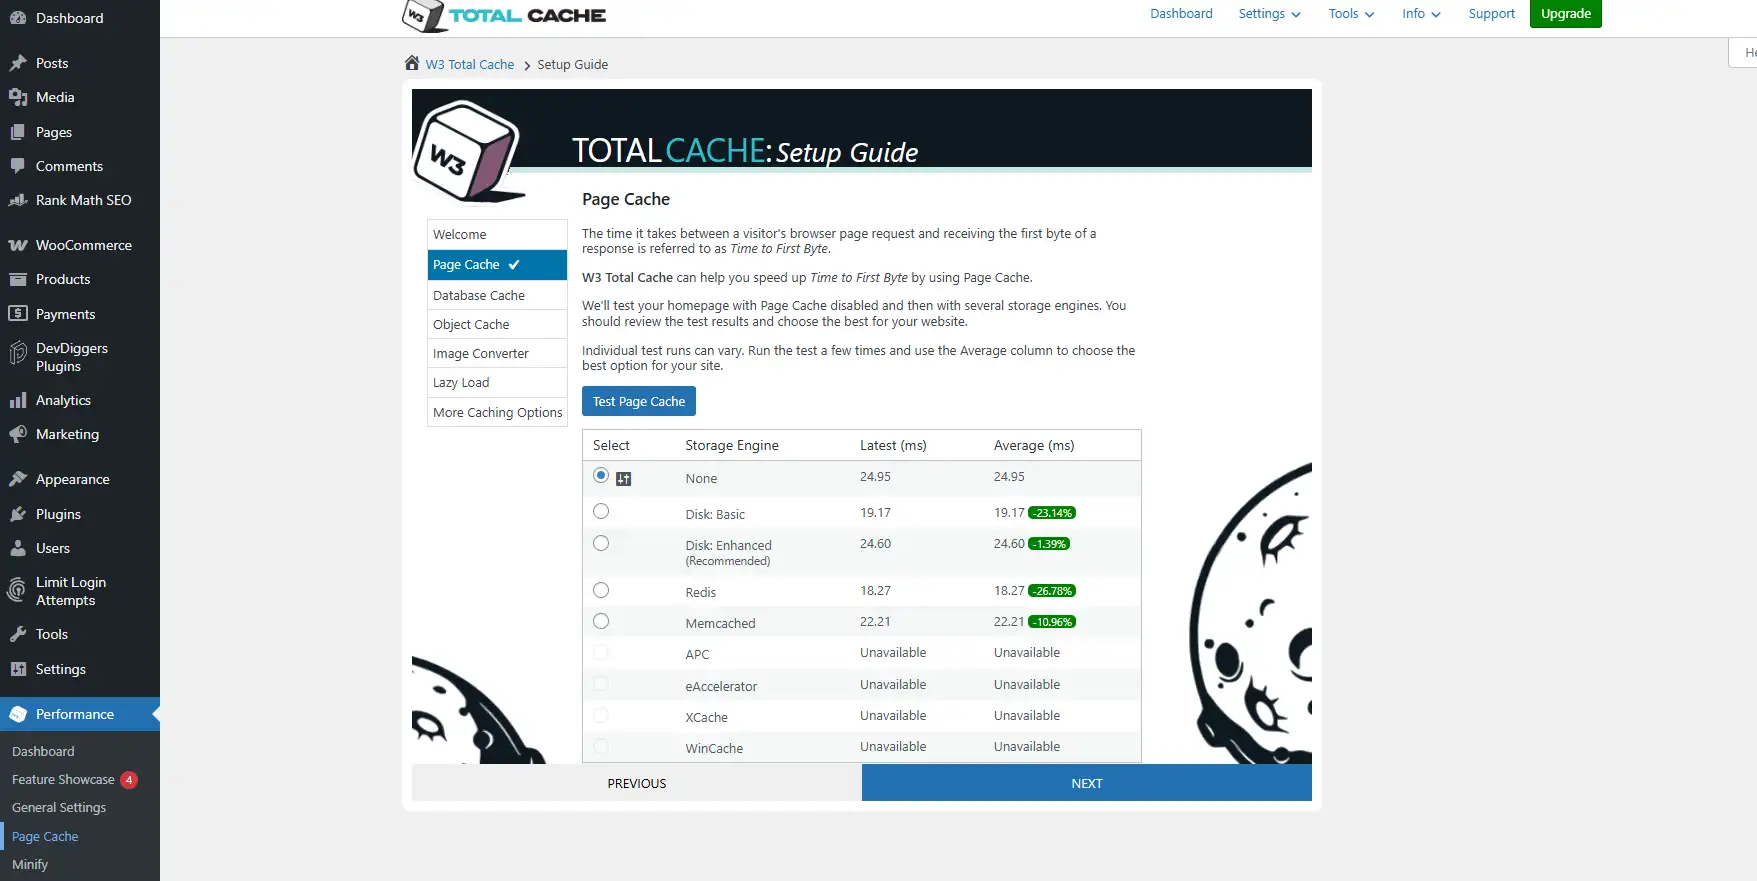
A cached response does not execute PHP or hit the database. Even during an attack, cached pages can continue serving while your server handles the flood.
Tools like WP Rocket, W3 Total Cache, or server-level caching via Redis object cache all reduce the per-request cost that makes application-layer attacks effective. For reducing TTFB and server load generally, our guide on reducing TTFB in WordPress walks through the options.
6. Add CAPTCHA to High-Risk Forms

Login pages, checkout, account registration, and comment forms are the first targets during an application-layer attack. Adding CAPTCHA (Google reCAPTCHA, Cloudflare Turnstile, or hCaptcha) to these forms adds friction that slows automated requests significantly. Our guide shows how to add Cloudflare Turnstile to WordPress step by step.
Our WooCommerce Advanced CAPTCHA plugin, built by DevDiggers, covers login, registration, checkout and product review forms. It works with Google reCAPTCHA, Cloudflare Turnstile or hCaptcha.
Layer 3: Monitoring and Early Warning
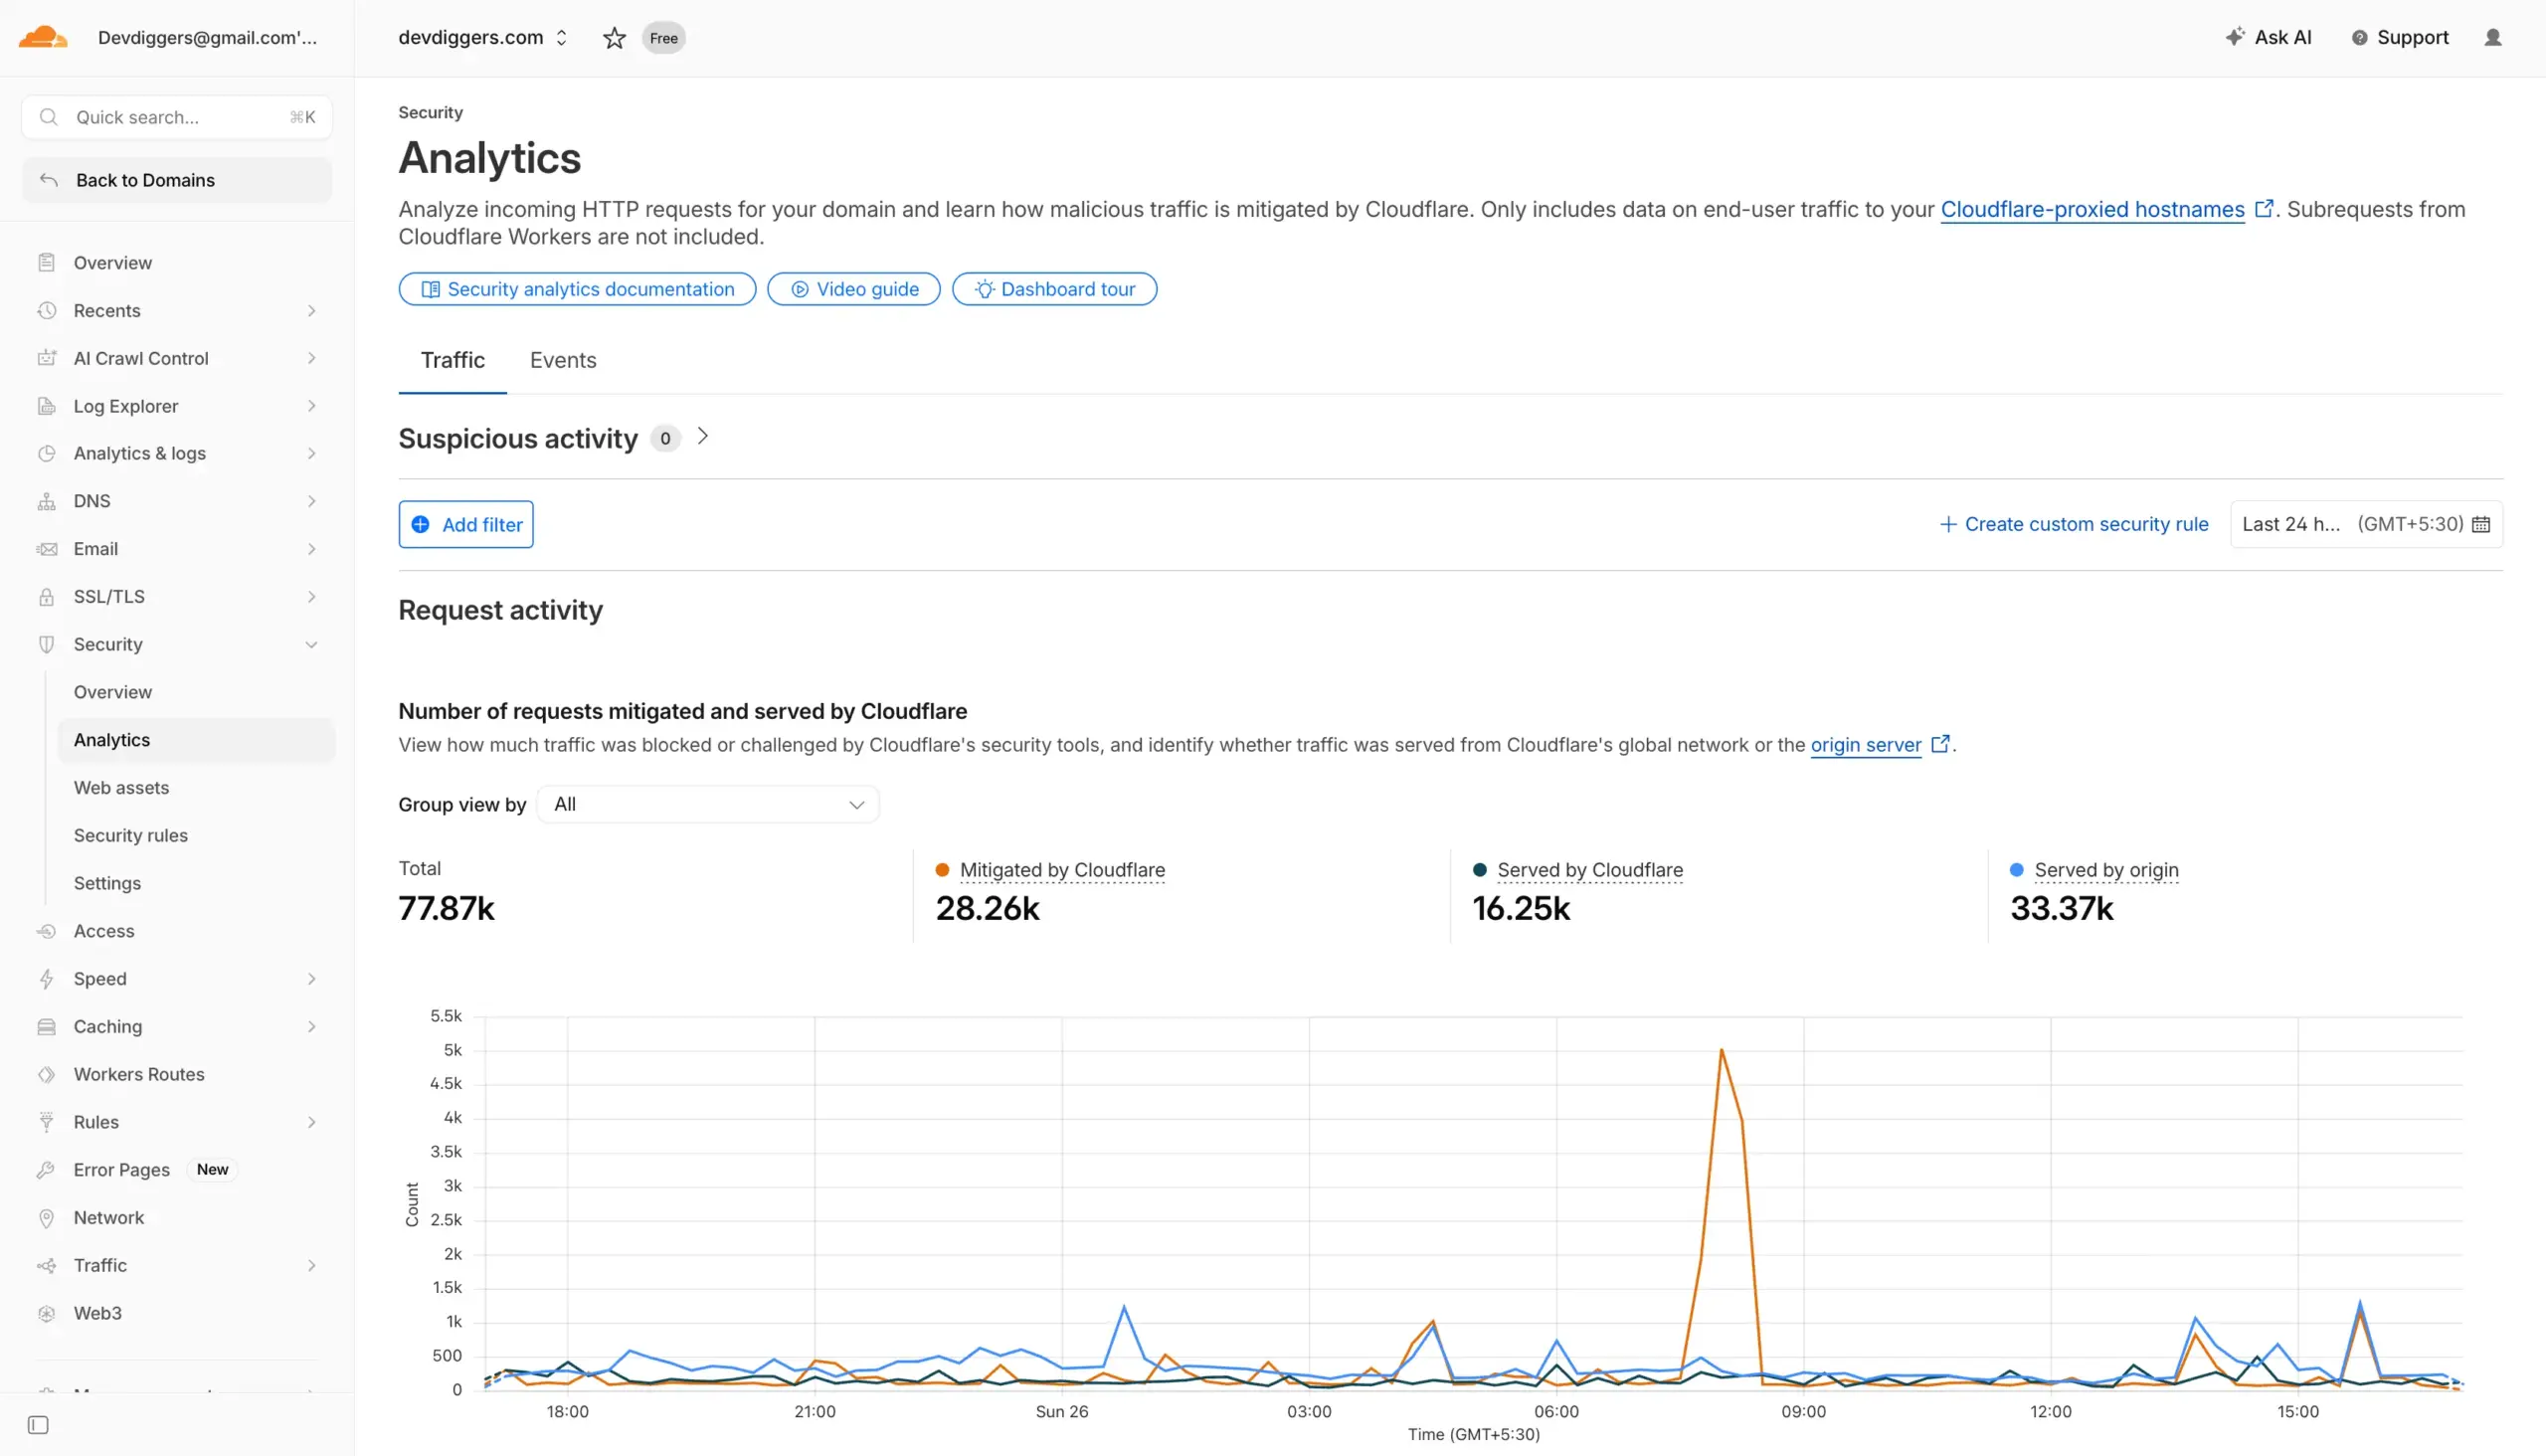
Protection is only as good as your ability to detect a problem early. Set up these monitoring points:
- Cloudflare Analytics or your CDN dashboard: Shows traffic volume, blocked requests, and threat scores in near real-time
- Wordfence activity log: Useful for spotting application-level patterns, even if it is not your primary DDoS defense
- Server access logs: The most detailed source, check request patterns to
/xmlrpc.php,/wp-login.php, and/wp-json/endpoints - Hosting provider alerts: Most managed WordPress hosts will alert you to unusual CPU or bandwidth spikes before you notice the slowdown
Large attacks are getting more common. Cloudflare counted 805 attacks above 1 Tbps in Q2 2026 alone. Set alerts that reach you by email or phone so you do not find out from customers.
What to Do During an Active WordPress DDoS Attack
Most guides tell you how to prevent an attack. Almost none tell you what to do once one is already happening. Here is a practical sequence.
- Contact your hosting provider first: Call or open a ticket immediately. Tell them what you are seeing. They have network-level tools you do not. They can identify traffic patterns, add temporary IP blocks at the server infrastructure level, and tell you whether the attack is volumetric or application-layer based on what they are seeing on their end.
- Enable “I’m Under Attack” mode in Cloudflare (if you use it): This adds a JavaScript challenge to every request. Real browsers pass it automatically. Bots do not. It will cause a brief delay for legitimate visitors, but it keeps your site accessible during most attacks.
- If you use Sucuri, tighten its security options: The Sucuri security options can block XML-RPC and limit the admin panel to allowlisted IP addresses.
- Check your server logs to identify the pattern: Look at which endpoint is being hit.
/xmlrpc.phpsuggests pingback or brute-force amplification./wp-login.phpis login flooding./wp-json/or a specific product or checkout URL suggests an application-layer attack targeting WooCommerce. The pattern tells you where to tighten rules. - Block concentrated IP ranges if possible: If the attack is coming from a narrow range of IP addresses or a single country, add a temporary block in your WAF. A fully distributed attack from thousands of unique IPs is harder to filter this way, but many attacks are less distributed than they appear.
- Do not make major configuration changes mid-attack: This is the step most people get wrong. Changing your theme, deactivating plugins at random, or reconfiguring your database during an active attack makes diagnosis harder and often creates new problems. Tighten rules at the WAF level. Avoid touching WordPress core settings until the attack subsides. If the attack is already underway, our WordPress security services can step in and read the logs.
- Prepare a communication plan: If you run a WooCommerce store, your customers need to know what is happening. A brief notice, “We’re experiencing higher than normal traffic and working to restore full service”, is better than a blank error page. If you have a team, assign one person to customer communication and keep others focused on technical response.
Most attacks are short. Cloudflare found that 90.6% of network-layer attacks in H1 2026 ended in under 10 minutes. If your layers are in place before the attack starts, most attacks pass without lasting damage. The real harm lands on unprotected sites and on owners who lose the first 30 minutes working out what is happening.
Common Mistakes That Leave WordPress Sites Exposed
Here is where most sites go wrong, even after “setting up protection.”
- Treating a security plugin as DDoS protection: Wordfence, Solid Security, and similar plugins are valuable tools. They scan for malware, block known bad IPs, and add login protection. But they are application-level. During a volumetric attack, your server is overwhelmed before these plugins process the request. They are part of a defense stack and not the whole stack.
- Blocking xmlrpc.php but leaving pingbacks on: The server rule only holds while it stays in place. A host migration or a plugin that reopens xmlrpc.php brings pingbacks back. Turn off pingbacks in
Settings > Discussionas well. - Disabling the entire REST API: As covered above, this breaks WooCommerce. Rate-limit and restrict specific endpoints instead.
- Using cheap shared hosting without DDoS mitigation: On shared hosting, you share a server with other sites. A DDoS attack targeting your site affects every other site on that server. Your hosting provider may suspend your account to protect others. Managed WordPress hosting with built-in DDoS mitigation costs more for a reason.
- Only watching wp-login.php: Most security dashboards highlight login attempt data because it is easy to collect. Attackers shifted significant effort to the xmlrpc.php and REST API endpoints years ago. If your monitoring only covers /wp-login.php, you have blind spots.
Patchstack’s State of WordPress Security in 2026 found that highly exploitable WordPress vulnerabilities rose 113% year over year in 2025. Gaps in your protection stack do not stay gaps for long.
Conclusion
WordPress DDoS protection is not one plugin or one setting. It is layers: a DNS-level WAF absorbs traffic before it reaches your server. WordPress hardening closes the xmlrpc.php, wp-login.php and REST API vectors, while caching and monitoring cut the cost of each request and catch problems early.
For WooCommerce stores, the stakes are higher because downtime during peak periods means direct revenue loss. The REST API trade-off matters. The WooCommerce-specific attack surface matters.
Start with edge-level protection, harden your WordPress installation, and have a clear plan for what to do if an attack starts. The sites that recover quickly are the ones that already know what to do before the attack happens.
Frequently Asked Questions
Q1. Does WordPress hosting with built-in DDoS protection replace a WAF?
Not entirely. Hosting-level DDoS protection handles volumetric attacks at the network layer, and it stops traffic floods before they reach your server. A WAF adds application-layer filtering, blocking malicious HTTP requests that look like legitimate traffic but are designed to exhaust your server’s PHP workers and database connections. You need both for full coverage. Many managed WordPress hosts include basic DDoS mitigation; very few include a full application-layer WAF.
Q2. How long do DDoS attacks on WordPress sites typically last?
Most are short. Cloudflare found that 90.6% of network-layer attacks in H1 2026 ended in under 10 minutes. Severe cases can last hours, and the most extreme attacks have run for days. The damage usually happens in the first few minutes if your defenses are not already in place. Always-on protection matters more than any reactive response you can run after the attack starts.
Q3. Can a small WordPress blog be targeted or is it only large sites?
Small sites get hit regularly. Attackers use automated tools that scan millions of sites looking for standard vulnerabilities: the default login URL, XMLRPC.php exposure, or missing rate limiting. Many attacks are not targeted at you specifically; your site just failed a vulnerability check that the botnet was running across the web. Small blogs are also targeted when they cover controversial topics, compete with a business, or happen to share a server with a high-value target.
Q4. Will enabling Cloudflare’s free plan protect my WooCommerce store from DDoS attacks?
Yes, for most attacks. Cloudflare’s free plan includes unmetered DDoS protection for layers 3 to 7, including HTTP floods. The free plan has one rate limiting rule and the Free Managed Ruleset. Pro and higher add the full Cloudflare Managed Ruleset. It is a good starting point, but not a complete solution for a store with real transaction volume.
Q5. Will my hosting provider suspend me if my WordPress site is used to attack other sites via pingback?
Yes, this happens. If your xmlrpc.php is open and attackers use your site’s pingback feature to flood a third-party target, your server is sending the malicious traffic. Your hosting provider may receive abuse complaints, see abnormal outbound traffic, and suspend your account to protect their network, even though you did not initiate the attack. Disabling or blocking xmlrpc.php at the server level closes this vector entirely and protects you from being an unwitting participant in someone else’s attack.